Username enumeration via subtly different responses
Username enumeration via subtly different responses
Platform: PortSwigger | Category: Authentication | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Authentication
Summary
Walkthrough of the PortSwigger Web Security Academy lab Username enumeration via subtly different responses (Authentication). This lab demonstrates a authentication vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Authentication
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
LAB 2 - Username enumeration via subtly different responses
Lab Description :
Solution :
Captured request -
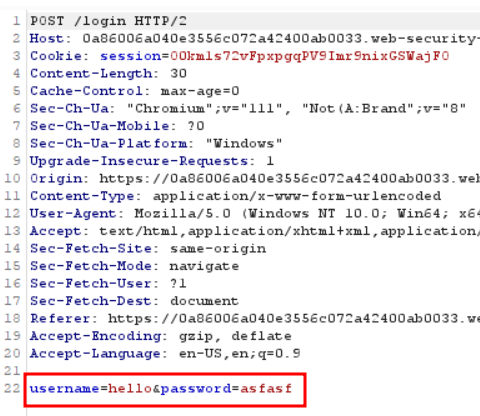
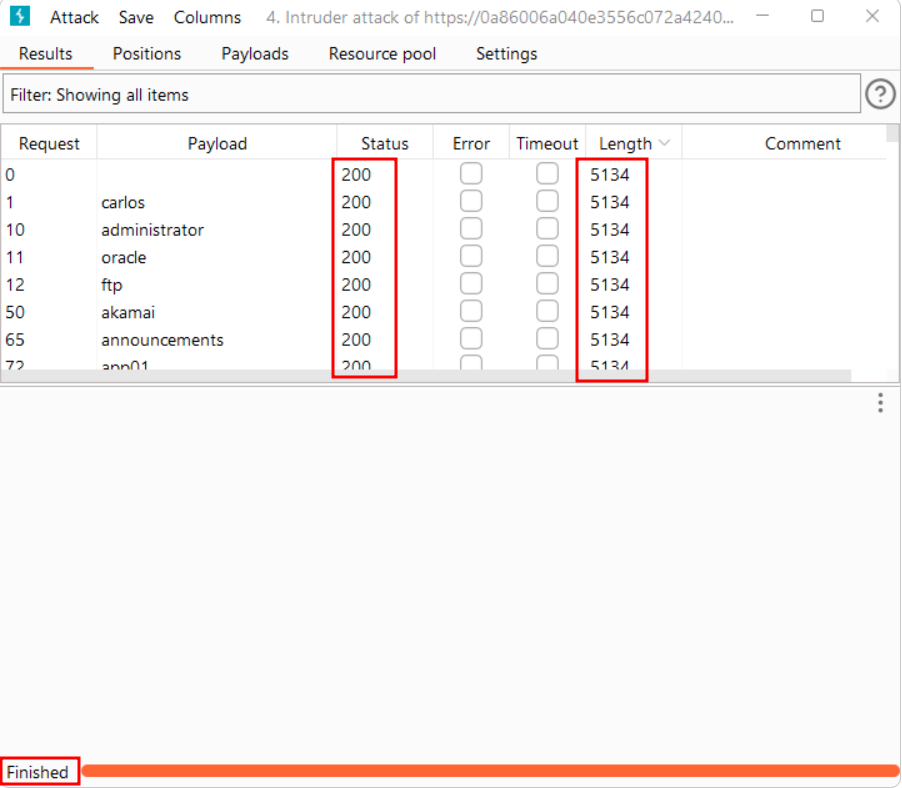
All the responses look then same.
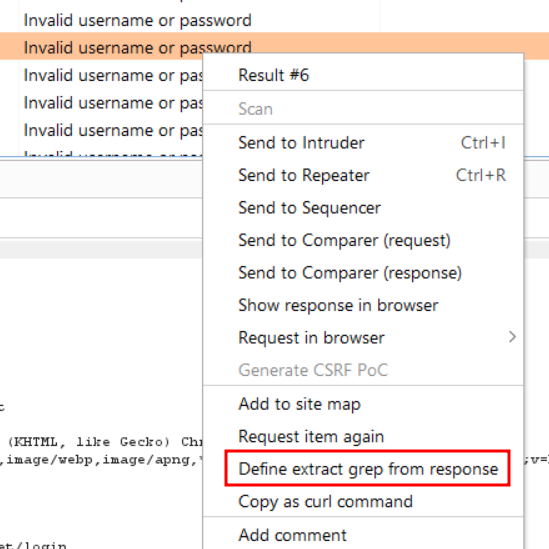
From this right click any one of the request -> Define extract grep from response option.
A new dialog box appears,
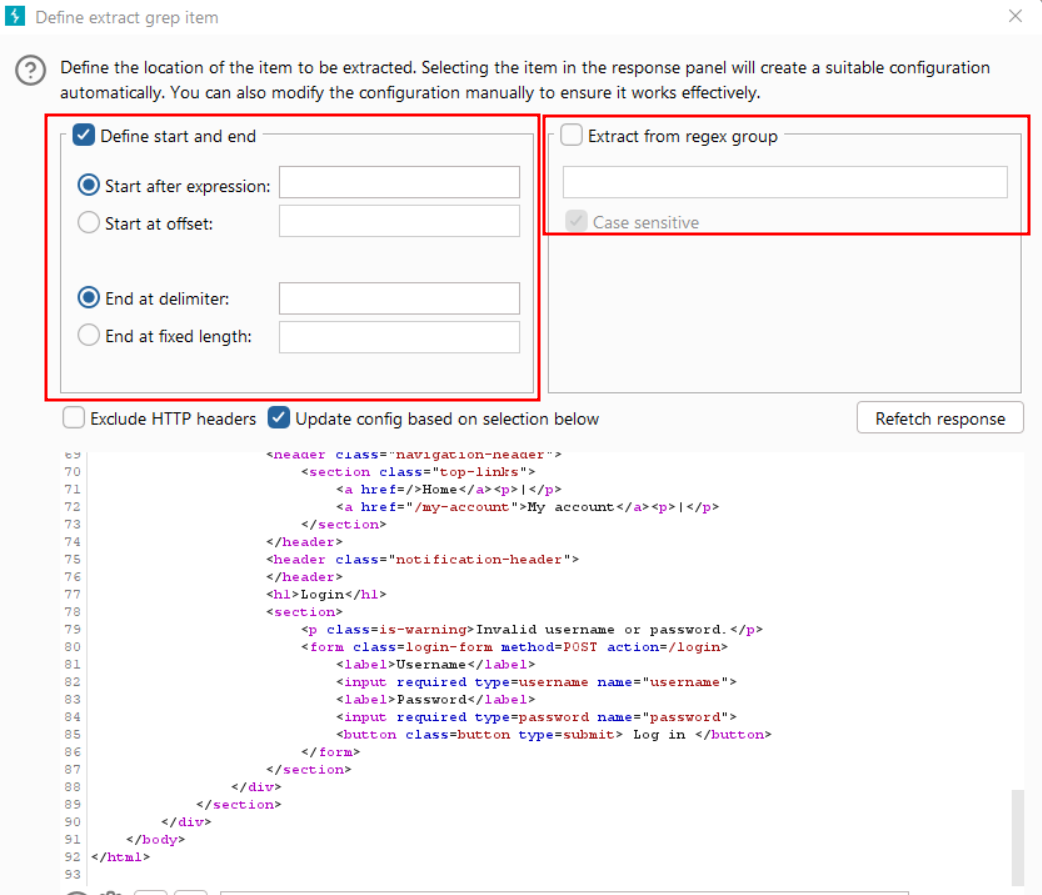
Scroll down & highlight Invalid username or password , the regex fields automatically gets updated.
Now start the attack,
We can see that there is a typo in only one response
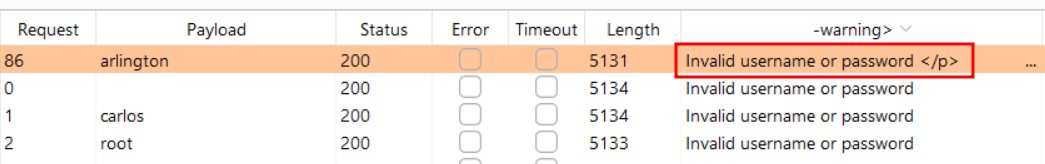
Here one thing stands out, this response has Invalid username or password rather than Invalid username or password ie.trailing fullstop & space is missing.
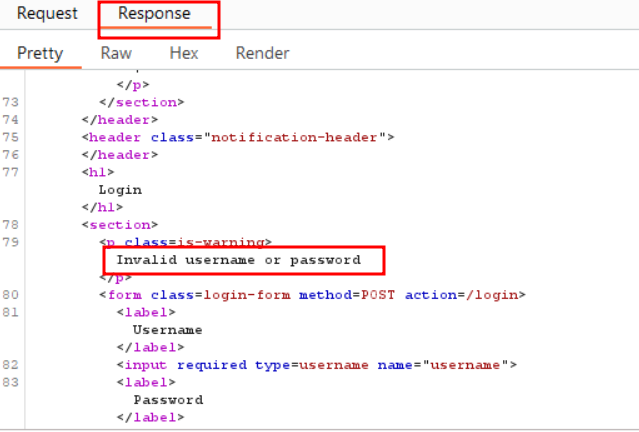
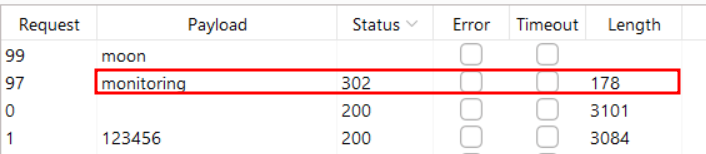
Now update the username to arlington , add the password field as target , add payload of passwords and start the attack.
We get a 302 status code which indicates that it is the password
Key Takeaways / Lessons
- Understanding Authentication detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Username enumeration via subtly different responses