2FA bypass using a brute-force attack
2FA bypass using a brute-force attack
Platform: PortSwigger | Category: Authentication | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Authentication
Summary
Walkthrough of the PortSwigger Web Security Academy lab 2FA bypass using a brute-force attack (Authentication). This lab demonstrates a authentication vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Authentication
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
As with passwords, websites need to take steps to prevent brute-forcing of the 2FA verification code. This is especially important because the code is often a simple 4 or 6-digit number. Without adequate brute-force protection, cracking such a code is trivial.
Some websites attempt to prevent this by automatically logging a user out if they enter a certain number of incorrect verification codes. This is ineffective in practice because an advanced attacker can even automate this multi-step process by creating macros for Burp Intruder. The Turbo Intruder extension can also be used for this purpose.
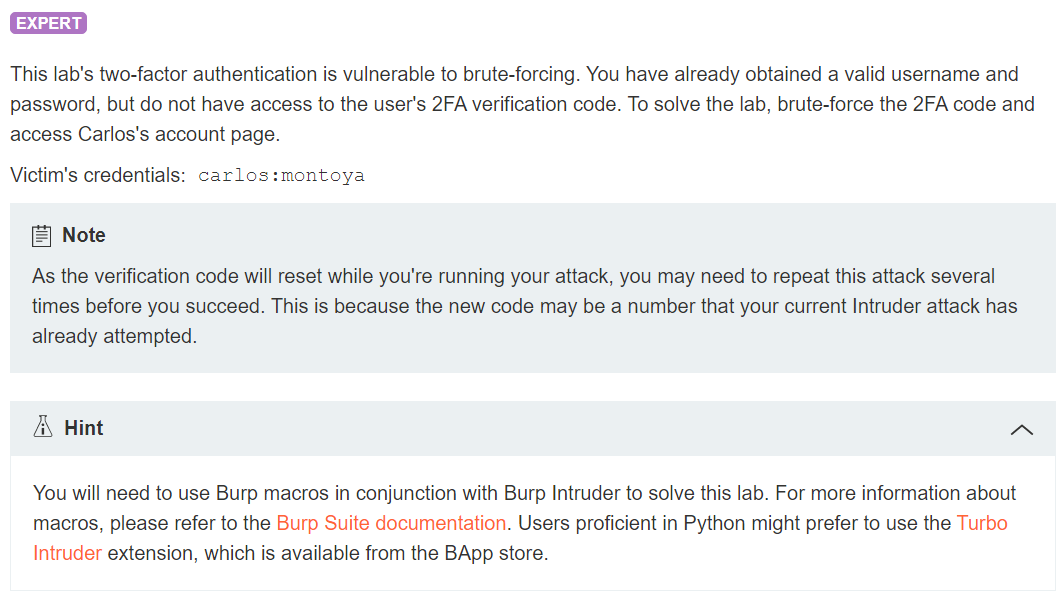
Lab Description :
Solution :
Blog on Burp Macros - https://akshita-infosec.medium.com/burp-macros-what-why-how-151df8901641
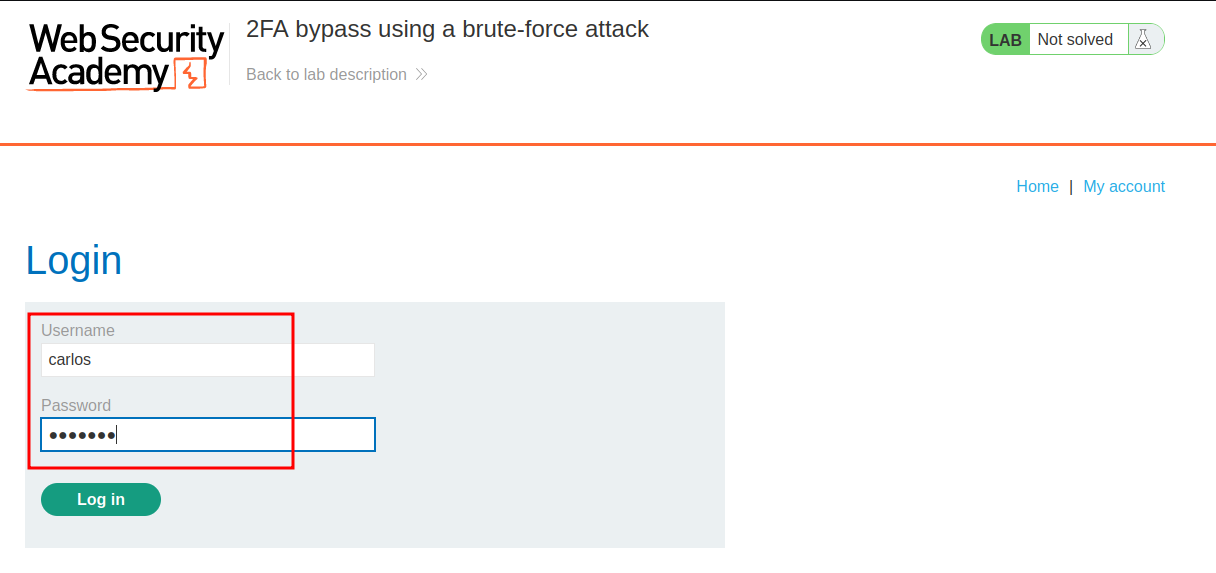
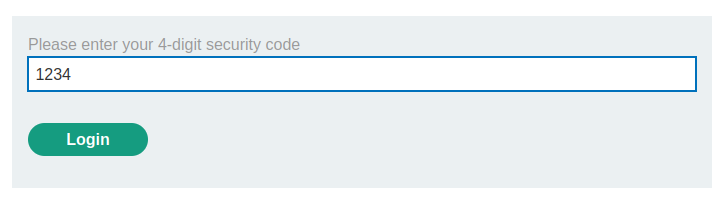
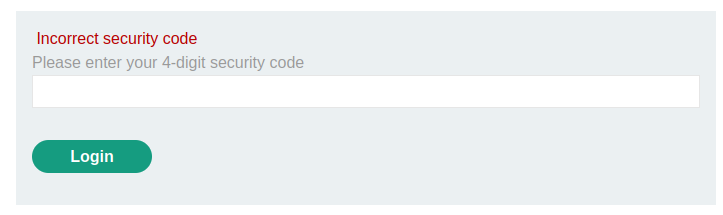
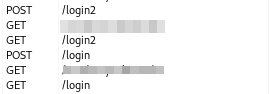
HTTP history
Project options -> Sessions tab
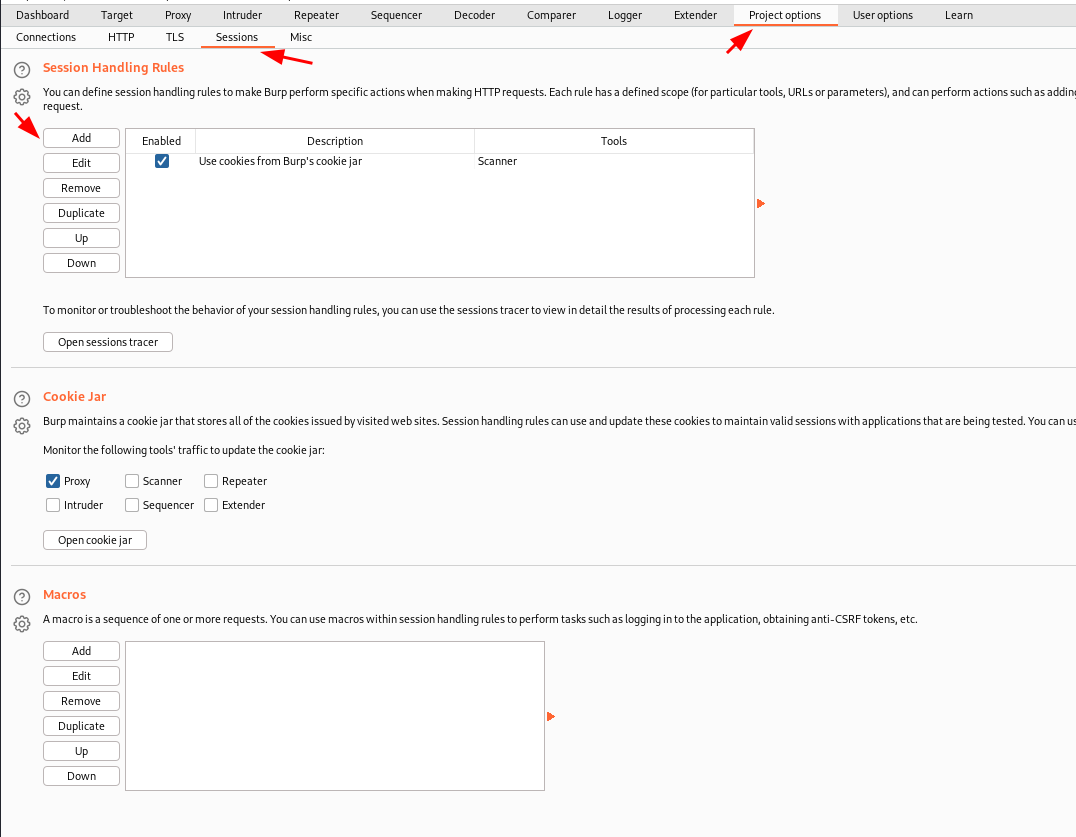
Under Session Handling Rules -> Add
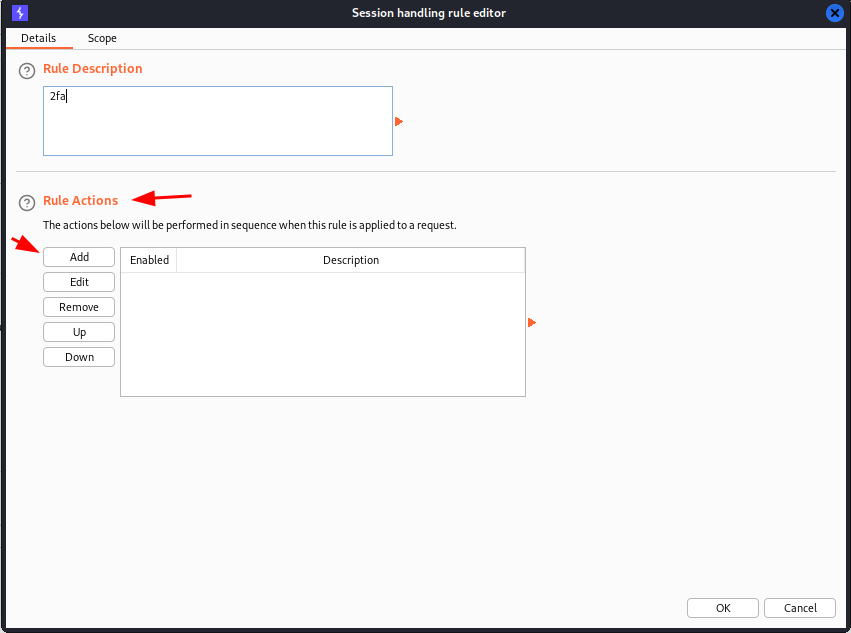
Click scope
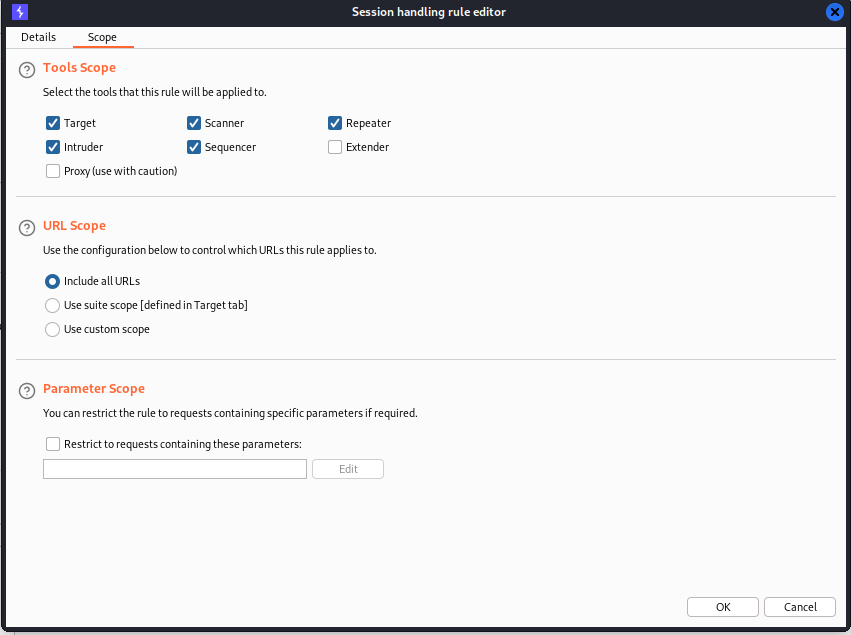
Go back to details tab
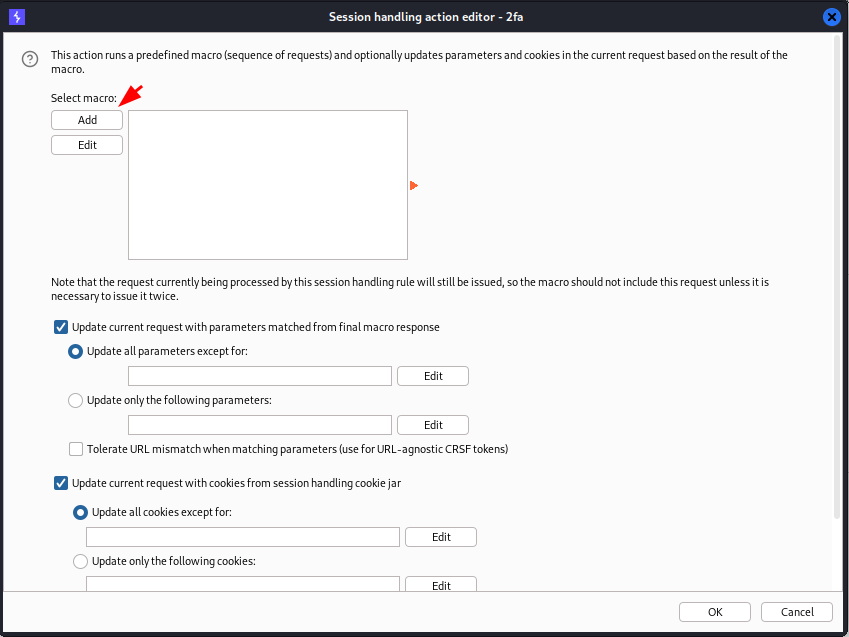
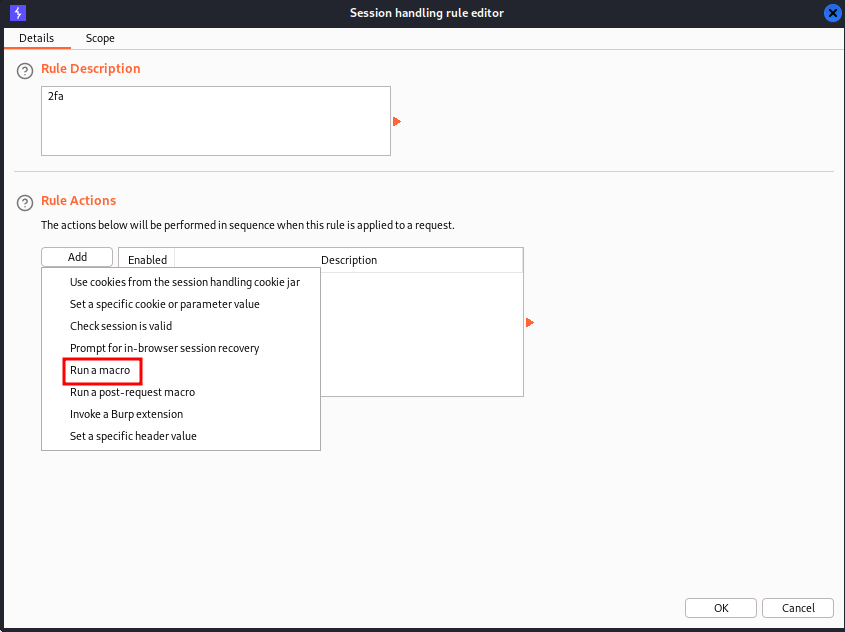
Key Takeaways / Lessons
- Understanding Authentication detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: 2FA bypass using a brute-force attack