Unprotected admin functionality
Unprotected admin functionality
Platform: PortSwigger | Category: Access Control | Type: Lab | Difficulty: N/A | OS: N/A | Author: XESXOR | Date: 2026-08-24 | Status: Solved Techniques: Web Security Academy, Access Control
Summary
Walkthrough of the PortSwigger Web Security Academy lab Unprotected admin functionality (Access Control). This lab demonstrates a access control vulnerability and its exploitation to achieve the lab objectives.
Lab Overview
PortSwigger Web Security Academy — Access Control
This writeup is part of the XESXOR PortSwigger collection. The original lab description and solution have been preserved and reformatted for clarity.
Lab Description :
Solution :
When the lab loads, we get the ususal shopping website.
Clicking on My Account page takes us to /login endpoint
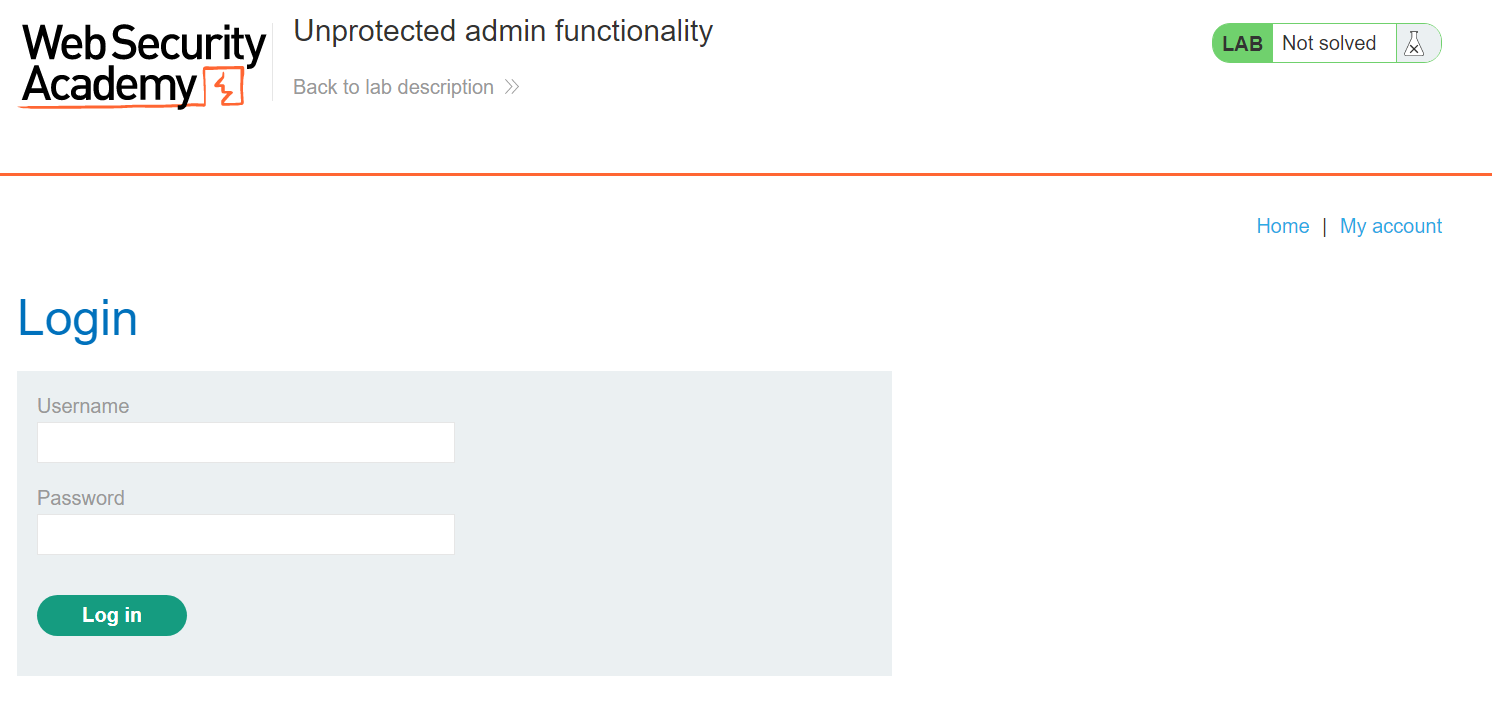
Now we need to bypass this login page and directly access the admin page.
For that we can look for one of the common web directories like the robots.txt and sitemap.xml
robots.txt
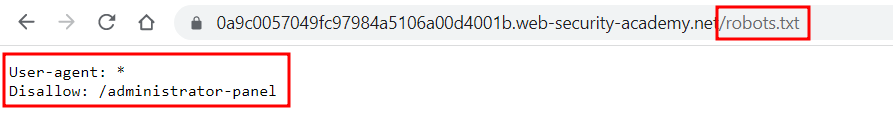
We see a disallowed login entry here for the admin panel which is /administrator-panel.
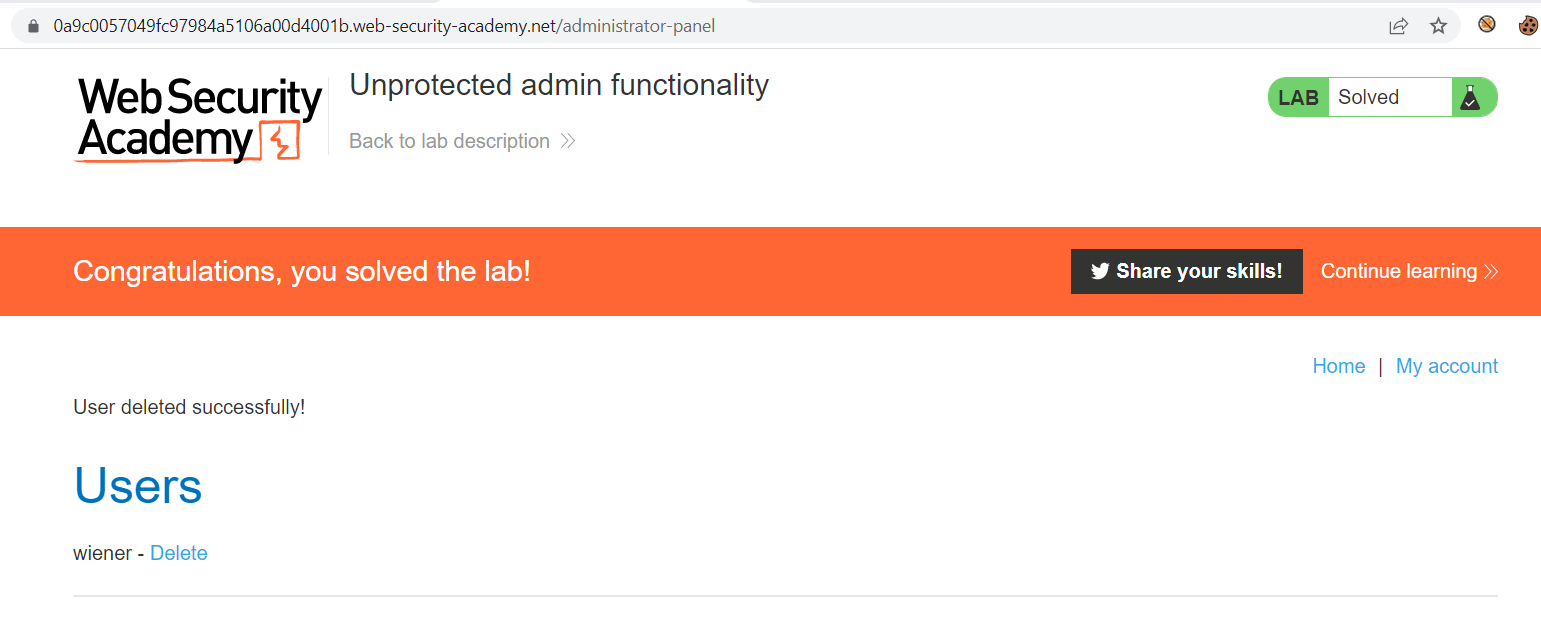
On visiting the /administrator-panel directory, we get the admin panel.
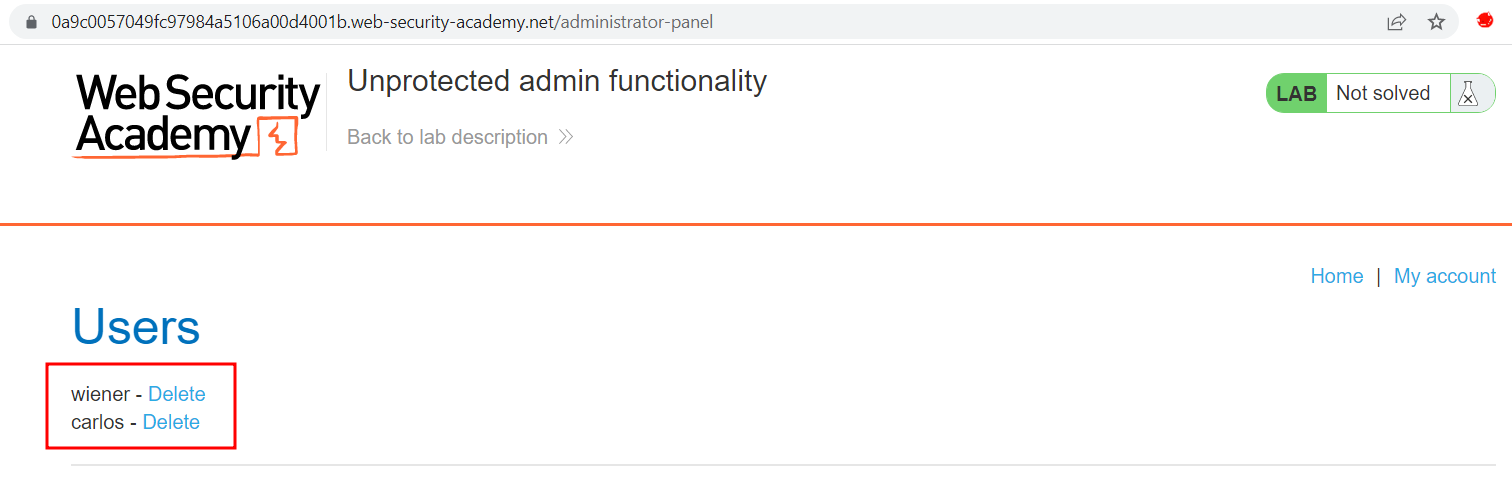
So we click the link to delete the user carlos to solve the lab.
Key Takeaways / Lessons
- Understanding Access Control detection and exploitation is crucial for web security.
- Always validate and sanitize user input; implement proper access controls.
- This lab is part of the PortSwigger Web Security Academy — practice in a safe, legal environment.
Crafted by XESXOR Research • 2026-08-24 • PortSwigger Web Security Academy • Lab: Unprotected admin functionality